 DATA
Minnesota Health Records Act: Patient Privacy, Tracking Pixels and Lawsuit Risk
A healthcare organization’s website can disclose patient information without anyone stealing a password or breaking into its network.
Latest from the Privacy Desk
All dispatches →The Federal Wiretap Act, 18 U.S.C. 2511(1): Privacy Lawsuit Risks and How to Protect Your Website
A single line of tracking code on a website can be treated as a surveillance device.
 DATA
New Hampshire Wiretap Act: Privacy Lawsuits, Tracking Pixels and Business Risk
A patient searches a hospital website for a specialist. A student signs into a university portal. A customer opens a support chat.
Song-Beverly Credit Card Act: When Checkout Data Collection Becomes a Privacy Lawsuit
A cashier asks for a ZIP code. A payment screen asks for a phone number. An electronic receipt requires an email address,…
Is Delaware Becoming the Strictest State Privacy Law? Why the DPDPA May Be More Restrictive Than California
For years, California has been treated as the benchmark for U.S.
Where There’s Smoke: Hinton v. Planned Parenthood and the “Linkage” Proof Gap in CIPA Pixel Class Actions
For more than three years, plaintiffs have filed California Invasion of Privacy Act (CIPA) claims against nearly every type of organization with…
 DATA
Privisy Review: What It Is, How It Works, and What It Costs
Most companies that worry about the California Consumer Privacy Act (CCPA) and its amendment, the California Privacy Rights Act (CPRA), eventually install…
 DATA
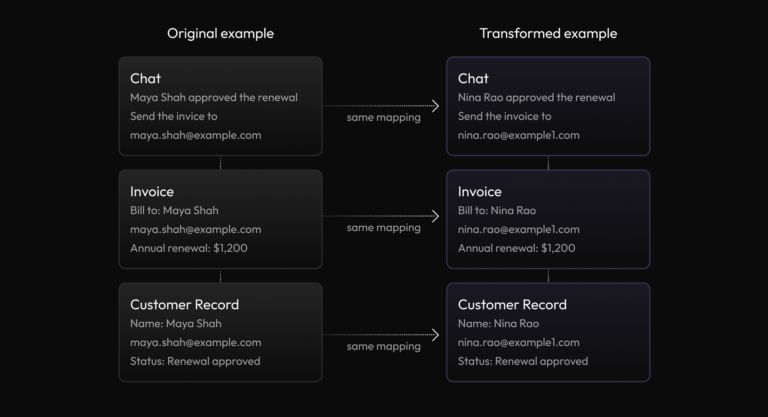
Can You Sell Your Company’s Data to Train Frontier AI? The Privacy Risks Behind the New Enterprise Data Market
The cleanest legal answer sounds simple: if information is truly anonymous, privacy law generally stops treating it as personal data.
 DATA
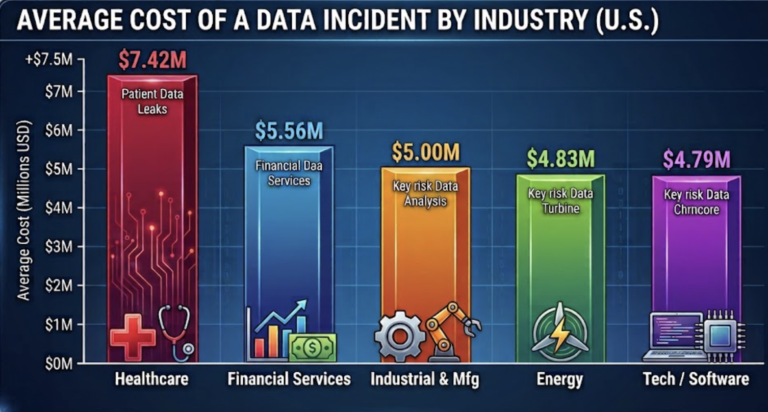
The Real Price of “Fix It Later”: Non-Compliance Now Costs U.S. Businesses $14.8 Million Per Enterprise
When corporate boards talk about data privacy, the conversation almost always lands on risk tolerance.
Privacy-Enhancing Technologies Are Moving From Theory to Infrastructure
For years, privacy programs have focused largely on controlling what organizations are allowed to collect.
The Specialty Was the Sensitive Field. Marketing Sent It Anyway
Doctoralia told investigators the pixels were for internal campaign measurement.
 DATA
UK High Court Clarifies DSAR Rules: You Owe the Data, Not Every Document
A U.K. High Court decision is giving privacy teams useful guidance on one of the most persistent problems in handling data subject…
 DATA
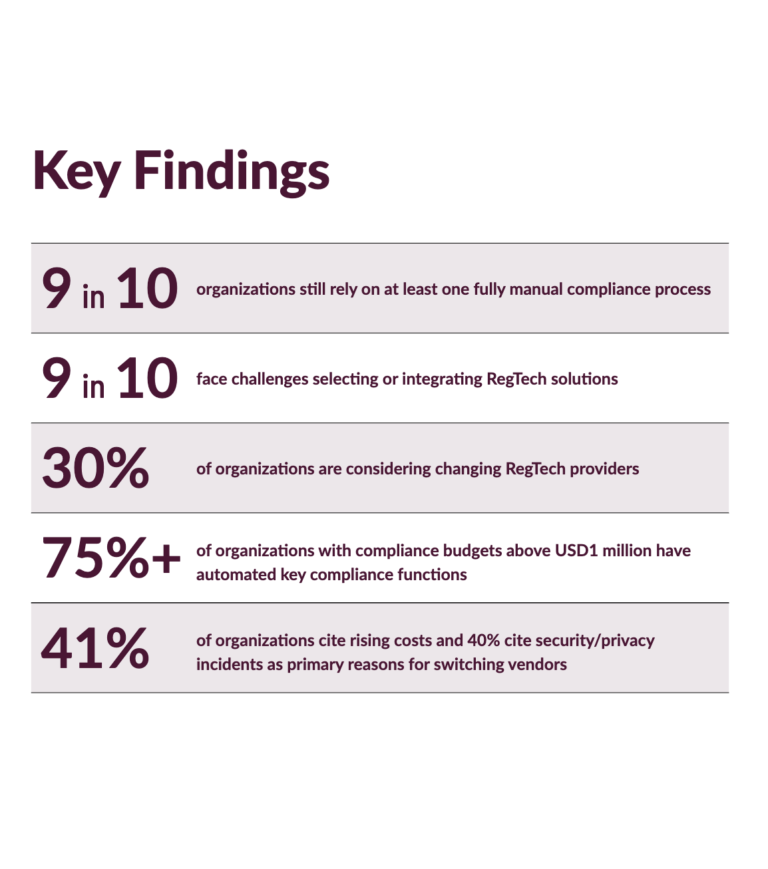
IAPP RegTech Report 2026: Privacy Teams Are Automating More, but the Human Work Is Not Going Away
Privacy technology is becoming more sophisticated, more automated and more deeply embedded in how companies manage compliance.