Topic · Governance Risk And Compliance
Every dispatch tagged Governance Risk And Compliance.
Cloud services complicate compliance with the EU’s NIS2 Directive and Digital Operational Resilience Act, or DORA.
Consider a hypothetical Monday morning disruption. A financial services company loses access to a SaaS platform used in a critical workflow. The provider posts a short status update,…
Latest from the Privacy Desk
All dispatches →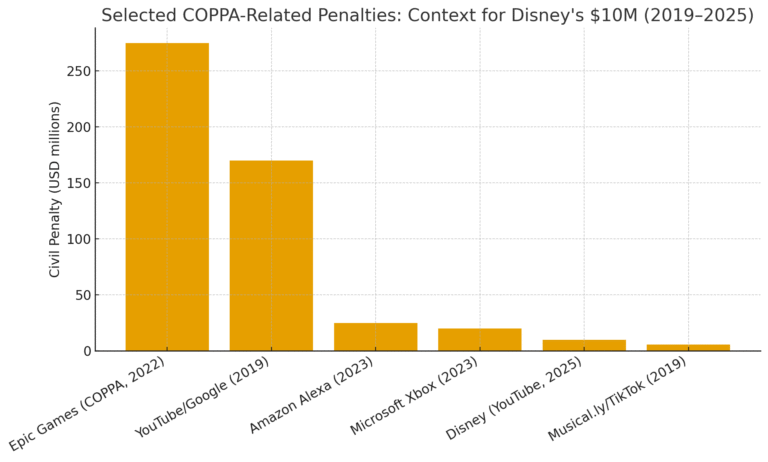 GOVERNANCE RISK AND COMPLIANCE
COPPA Is Quietly Becoming the Backbone of U.S. Kids’ Online Safety
It is easy to treat the Children’s Online Privacy Protection Act as a relic.
 GOVERNANCE RISK AND COMPLIANCE
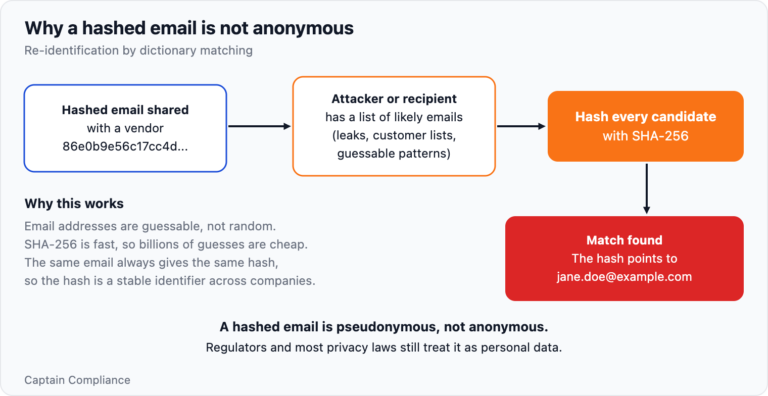
Hashing Algorithm: What It Is, How It Works, and Why It Matters for Data Privacy
A hashing algorithm is a mathematical function that converts input data of any size into a fixed-length string of characters called a…
DHS Watchdog: Most Civilian Agencies Missed CISA’s Cloud Security Order, and CISA Cannot Make Them Comply
The Department of Homeland Security Office of Inspector General says most federal civilian agencies missed the cloud-security rules CISA told them to…
3PDD Meaning: What Third-Party Due Diligence Actually Requires, and Why Most Programs Fall Short
The IDScan breach that exposed driver’s license data for more than 150 million people wasn’t a failure at the businesses whose customers…
 GOVERNANCE RISK AND COMPLIANCE
NYDFS Does Not Want Your Annual PDF. It Wants the Decision Trail.
The Department’s September 10 industry letter creates no new Part 500 duties.
Grindr Will Pay £26 Million to End a UK Group Claim That Its Pre-2020 Ad Stack Carried HIV Status
Grindr Inc. agreed on September 2 to pay £26 million to resolve a group action in the High Court of England and…
 GOVERNANCE RISK AND COMPLIANCE
US Police Memos Treat Meta Smart Glasses as a Facility and Counterintelligence Risk
The Guardian reported on September 8 that it reviewed about a dozen previously unreported law-enforcement documents, obtained by the transparency group Property…
 GOVERNANCE RISK AND COMPLIANCE
TaxAct’s $275,000 Privacy Settlement Shows Regulators Are Moving From Privacy Policies to Continuous Tracker Monitoring
A new privacy settlement involving TaxAct, Meta and Google offers businesses one of the clearest examples yet of how regulators expect companies…
 AI
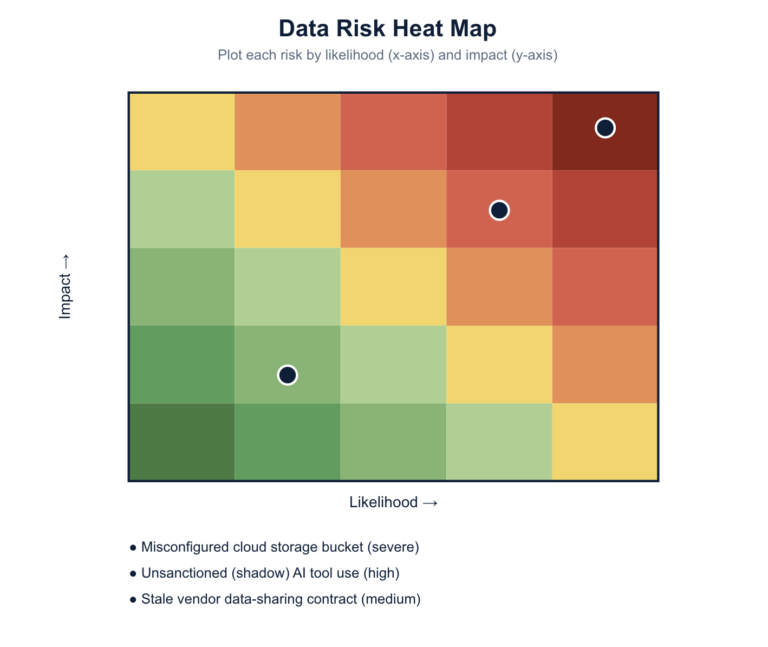
The Data Risk Management Framework Built for the Shadow AI Era
The global average cost of a data breach just hit $4.99 million — a 12% jump and a record high, according to…
Herbert Smith Freehills Kramer, Goodwin Procter, Blank Rome and More Disclose Data Breaches as Law Firm Cyberattacks Continue
At least three major law firms—Herbert Smith Freehills Kramer, Goodwin Procter, and Stettinius & Hollister—disclosed data breaches to U.S.
 GOVERNANCE RISK AND COMPLIANCE
Consumer Reports Finds Major Crypto Exchanges Fall Short on Privacy, Transparency, and Risk Disclosure
Consumer Reports has released a multi-month evaluation of five major U.S.-facing cryptocurrency exchanges—Binance.US, Coinbase, Crypto.com, Gemini, and Kraken—concluding that the platforms make…
Senate HELP Committee Advances Bill Extending HIPAA-Style Protections to Consumer Health Data and Wearables
The Senate Committee on Health, Education, Labor and Pensions voted 22-0 to advance an amended version of the Health Information Privacy Reform…