Topic · Compliance
Every dispatch tagged Compliance.
 COMPLIANCE
Hospitals Warn HHS Not to Ban App Authorization Checks in the Coming HIPAA Final Rule
Hospital IT leaders are trying to head off a HIPAA change that has not been published yet.
Latest from the Privacy Desk
All dispatches → COMPLIANCE
AI-Written Subject Access Requests: What the ICO Expects Organisations to Do
Privacy teams across the UK have noticed a change in their inboxes: subject access requests that run to several pages, cite laws…
 GDPR
EDPB Finalises Its Legitimate Interest Guidelines: A Practical LIA Walkthrough
Europe’s data protection authorities have finished their rewrite of the most argued-over legal basis in the GDPR.
 AI
England’s Proposed EdTech and AI Safety Certification: What Suppliers Should Start Evidencing Now
England’s Proposed EdTech and AI Safety Certification: What Suppliers Should Start Evidencing Now Schools in England buy software the way many small…
UK Under-16 Social Media Ban Could Reach YouTube Kids: What Child-Focused Services Should Check Now
When the UK government announced in June that under-16s would be barred from social media, services built for children appeared to be…
 AI
Macron Wants AI Banned Where It Threatens Children. The Paris Charter Asks for Testing Instead
France is trying to turn children’s safety into the first piece of what President Emmanuel Macron calls “frontier AI regulation.” In an…
 COMPLIANCE
EU Digital Fairness Act Draft: What UX, Consent and Marketing Teams Should Audit Now
The European Commission presented its Digital Fairness Act proposal on Wednesday, November 11, 2026, confirming what leaked drafts had shown.
Customer Data Platforms Compared: Privacy, Consent and Compliance Guide
A customer data platform, or CDP, collects customer data from your website, apps and other sources, builds unified profiles, and sends that…
 DATA
Why Pixel Tracking Is Usually Not a Civil Code 1798.82 Data Breach
California’s breach-notification statute is meant for a specific emergency: computerized personal information has been acquired without authorization because the security of a…
 CALIFORNIA PRIVACY – CPRA
CalOPPA Privacy Policy Disclosures and the Meta Pixel
The California Online Privacy Protection Act is one of the country’s older website-privacy rules, and it is easy to forget because newer…
 LAW FIRMS
Wire Fraud Allegations in Meta Pixel Demand Letters
Federal wire fraud is a serious crime. It is the statute prosecutors use when someone runs a scheme to obtain money or…
 COMPLIANCE
How Meta Pixel Demand Letters Use the FTC Act as a Crime-Tort Predicate
Section 5 of the Federal Trade Commission Act is one of the most important consumer-protection rules in American law.
 LAW FIRMS
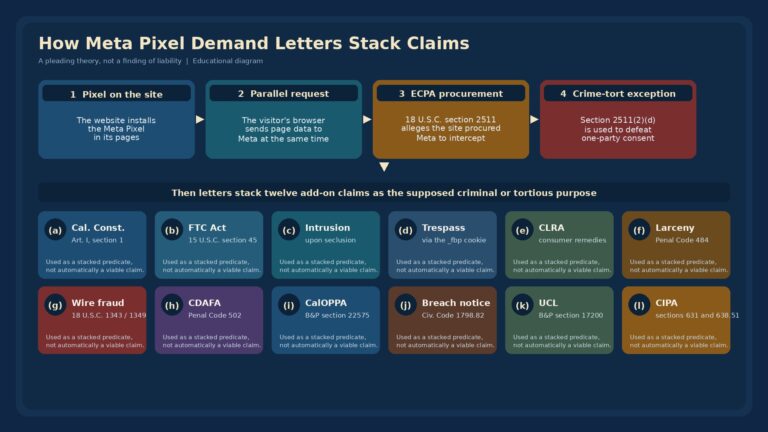
How Plaintiff Firms Use Meta Pixel Demand Letters: ECPA Procurement, the Crime-Tort Exception, and Twelve Add-On Claims
Demand letters built around the Meta Pixel are no longer limited to a single California wiretap statute.