Privacy law, enforcement and technology—coverage for everyone in the privacy field.
Practical analysis of privacy litigation, website tracking, AI governance, global regulation and the technology organizations use to manage risk.
Latest from the Privacy Desk
All dispatches →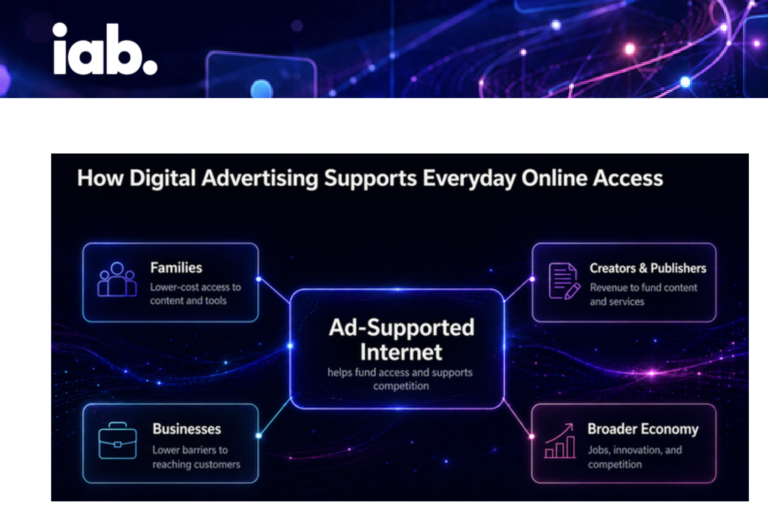 GOVERNANCE RISK AND COMPLIANCE
IAB Proposes a Proportionate Framework for Modernizing U.S. Children’s Privacy Law
The Interactive Advertising Bureau (IAB) has entered the heated debate over children’s and teens’ online privacy with a detailed policy blueprint.
 GDPR
EDPB Orders Belgian Regulator to Hear NOYB Cookie Banner Complaint on the Merits
A Belgian regulator attempted to dismiss a cookie-banner complaint without deciding whether the banner was lawful.
 DATA
Mozilla Tested Six Period Tracker Apps. Only One Earned a Perfect Privacy Score
Period-tracking applications ask users to record some of the most intimate information a technology company can collect.
 AI
EU Cloud Sovereignty Framework Compliance
Digital sovereignty has spent years sounding more like a political ambition than a measurable compliance standard.
 CALIFORNIA PRIVACY – CPRA
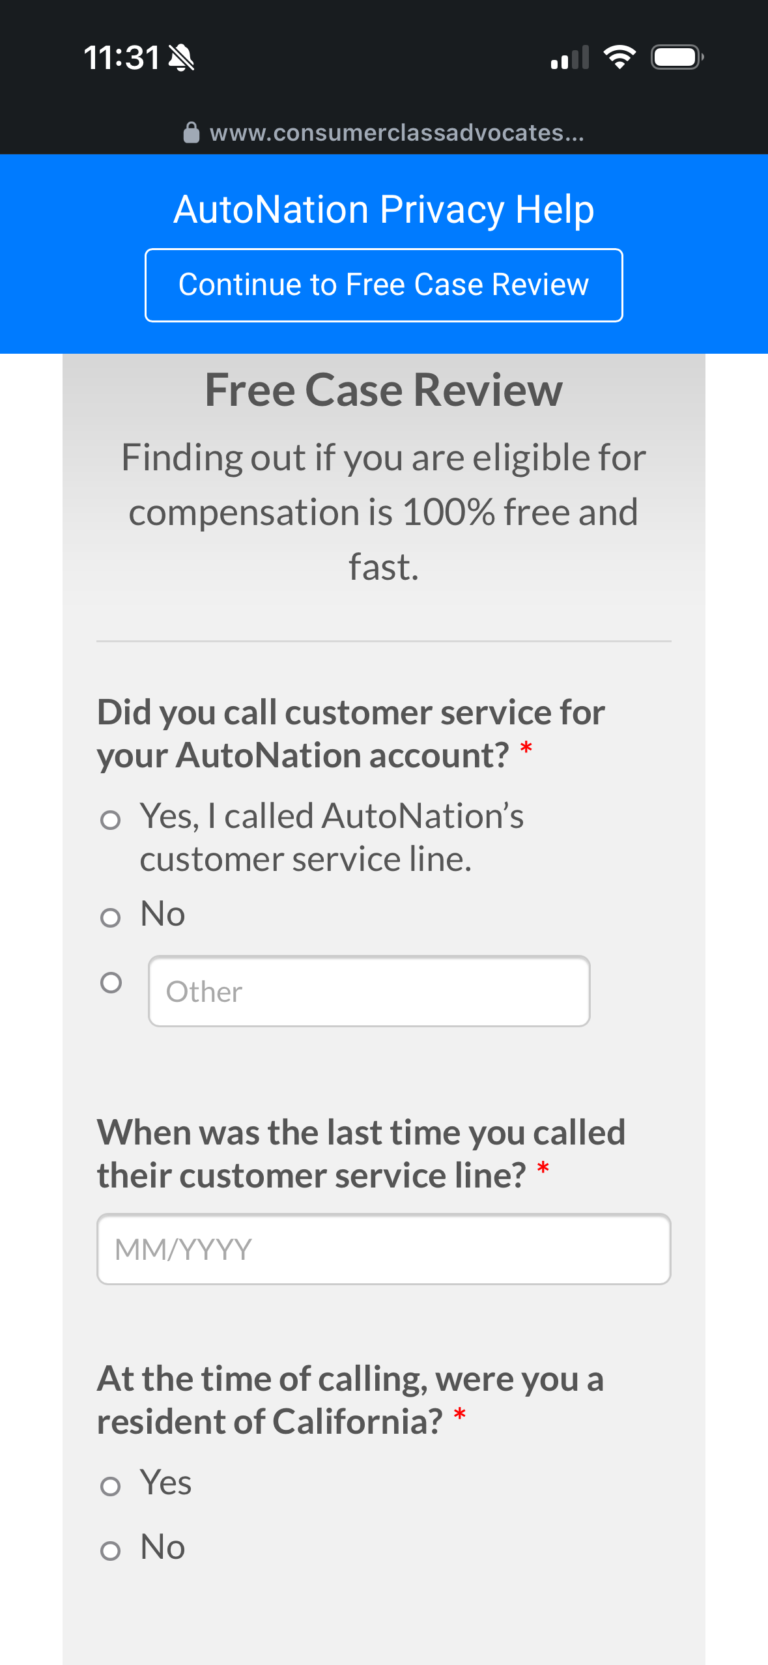
Autonation Privacy Case Dismissed But New Ads Show Ongoing Privacy Litigation Risks Your Company Can Protect Against
Autonation just beat a CIPA case based on jurisdiction grounds but constant threats are lurking each and every week with new ads…
EDPB’s Landmark Guidelines on Anonymisation, AI Web Scraping, and Blockchain
Being called a A New Era of Clarity and Accountability: The European Data Protection Board (EDPB) has taken a major step forward…
 AI
Auditing AI: Why Internal Audit Is the Next Front Line of AI Compliance
Artificial intelligence has stopped being the shiny thing in the innovation lab.
Blank Rome Hit with Class Action Over Law Firm Data Breach: Another Wake-Up Call for Legal Industry Cybersecurity
Law firms continue to be prime targets for cybercriminals, and the latest high-profile case involves Blank Rome.
USANTIS: EU Representative Under Article 27 GDPR
A guest post by USANTIS USANTIS acts as the EU representative under Article 27 GDPR for companies based outside the EU.
 GDPR
CNIL Steps Up Enforcement with 23 New Sanctions Under Simplified Procedure
The French data protection authority, the CNIL, has significantly ramped up its use of the simplified sanctioning procedure in 2026.
China Tightens the Reins on AI: New Rules Target Ethics, Emotional Chatbots, and Autonomous Agents
China just dropped a trio of targeted AI regulations in July 2026 that signal a clear evolution in how the country is…
New Jersey’s A5328: The Data Broker Law That Comes for Companies With Direct Consumer Relationships
Being framed as the most dangerous data broker law for business owners who do not consider themselves data brokers yet will share…