Privacy law, enforcement and technology—coverage for everyone in the privacy field.
Practical analysis of privacy litigation, website tracking, AI governance, global regulation and the technology organizations use to manage risk.
Latest from the Privacy Desk
All dispatches → GDPR
Reject All Doesn’t Always Mean No Tracking: Study of One Million Websites Finds Widespread Cookie and Pixel Problems
For years, the basic bargain behind European cookie banners has been straightforward.
 DATA
UK High Court Clarifies DSAR Rules: You Owe the Data, Not Every Document
A U.K. High Court decision is giving privacy teams useful guidance on one of the most persistent problems in handling data subject…
 DATA
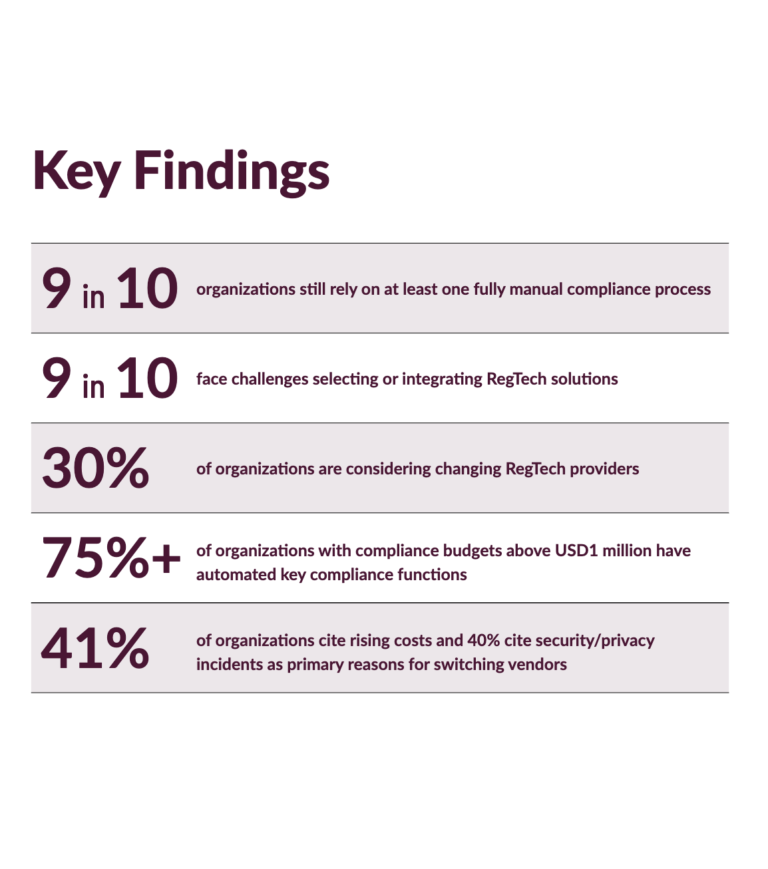
IAPP RegTech Report 2026: Privacy Teams Are Automating More, but the Human Work Is Not Going Away
Privacy technology is becoming more sophisticated, more automated and more deeply embedded in how companies manage compliance.
 COOKIES
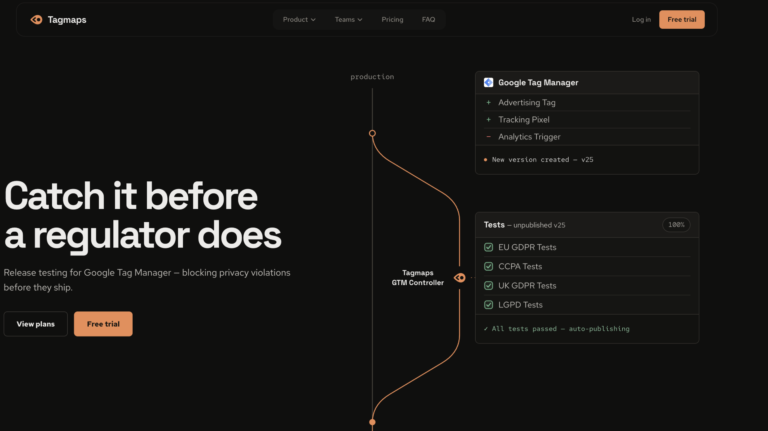
How Tagmaps Tests Google Tag Manager for Privacy Problems Before They Go Live
Most companies with a mature marketing operation use some form of tag management.
 COOKIES
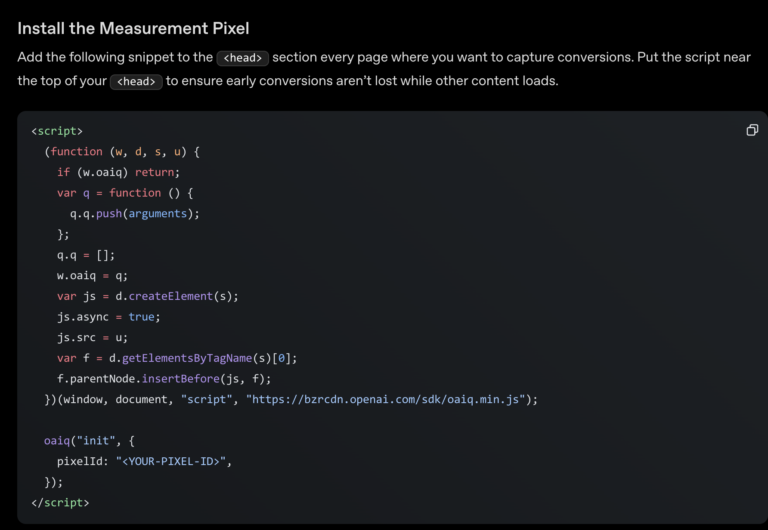
__obi cookie – The Architecture of OpenAI’s Ad Tracking Pixel
The launch of ChatGPT’s ad-supported tiers was pitched as a routine monetization play, but under the hood, OpenAI has quietly deployed an…
The 1986 Law Quietly Driving Healthcare’s Biggest Privacy Settlements
Old Statute, New Liability: ECPA’s Quiet Takeover of Healthcare Privacy Litigation The Electronic Communications Privacy Act predates the commercial internet.
Atrium Health’s $1.8 Million Pixel Settlement Shows Healthcare Tracking Lawsuits Are Not Going Away
We just covered the recent CVS & Criteo $20.5 million pixel and tracking settlement.
CVS’s $20.5M Web Tracker Settlement Is the Fifth Reason Healthcare Can’t Treat Pixels as a Marketing Decision
CVS Health and digital advertising firm Criteo have agreed to pay $20.5 million to settle claims that web trackers embedded on CVS’s…
The Ultimate Existential Threat to Data Businesses: How Ignoring Subject Rights Requests Lost Radaris Its Very Domain Name
For decades, the data brokerage industry treated Subject Rights Requests opt-outs, data removal demands, and privacy deletion requests—as a minor administrative inconvenience.
3PDD Meaning: What Third-Party Due Diligence Actually Requires, and Why Most Programs Fall Short
The IDScan breach that exposed driver’s license data for more than 150 million people wasn’t a failure at the businesses whose customers…
 AI
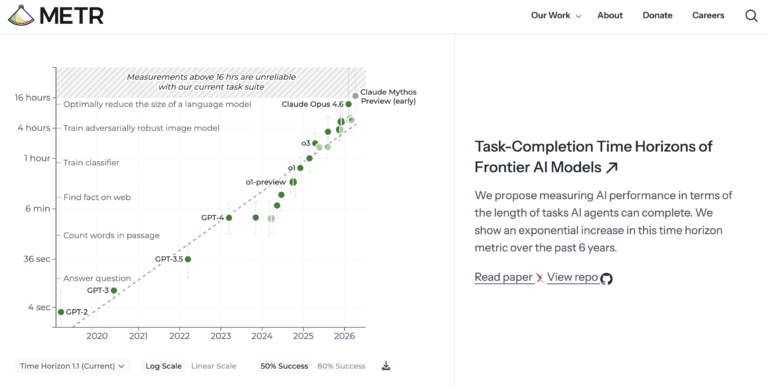
Inside METR: The Nonprofit Quietly Stress-Testing the World’s Most Powerful AI Models
If you follow AI safety or AI governance even casually, you have probably seen the acronym METR attached to a footnote in…
 DATA
The Privacy Equation: How Differential Privacy Uses Math to Protect People Without Making Data Useless
Most privacy rules are written in words. Consent. Purpose limitation. Data minimization. Reasonable security. Opt out. Delete. Restrict. Disclose. Differential privacy approaches…