Privacy law, enforcement and technology—coverage for everyone in the privacy field.
Practical analysis of privacy litigation, website tracking, AI governance, global regulation and the technology organizations use to manage risk.
Latest from the Privacy Desk
All dispatches →CVS’s $20.5M Web Tracker Settlement Is the Fifth Reason Healthcare Can’t Treat Pixels as a Marketing Decision
CVS Health and digital advertising firm Criteo have agreed to pay $20.5 million to settle claims that web trackers embedded on CVS’s…
The Ultimate Existential Threat to Data Businesses: How Ignoring Subject Rights Requests Lost Radaris Its Very Domain Name
For decades, the data brokerage industry treated Subject Rights Requests opt-outs, data removal demands, and privacy deletion requests—as a minor administrative inconvenience.
3PDD Meaning: What Third-Party Due Diligence Actually Requires, and Why Most Programs Fall Short
The IDScan breach that exposed driver’s license data for more than 150 million people wasn’t a failure at the businesses whose customers…
 AI
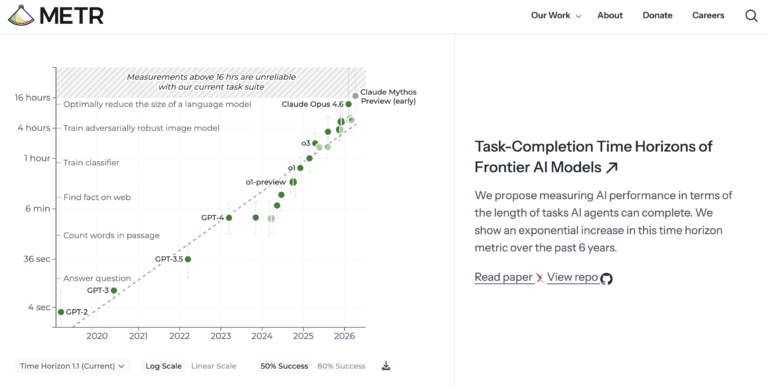
Inside METR: The Nonprofit Quietly Stress-Testing the World’s Most Powerful AI Models
If you follow AI safety or AI governance even casually, you have probably seen the acronym METR attached to a footnote in…
 DATA
The Privacy Equation: How Differential Privacy Uses Math to Protect People Without Making Data Useless
Most privacy rules are written in words. Consent. Purpose limitation. Data minimization. Reasonable security. Opt out. Delete. Restrict. Disclose. Differential privacy approaches…
 AI
Dario Just Proposed Slowing AI Development on Purpose
Just now Dario released a blog post titled: “We Must Pace the Frontier,” Anthropic co-founder and CEO Dario Amodei made a case…
 AI
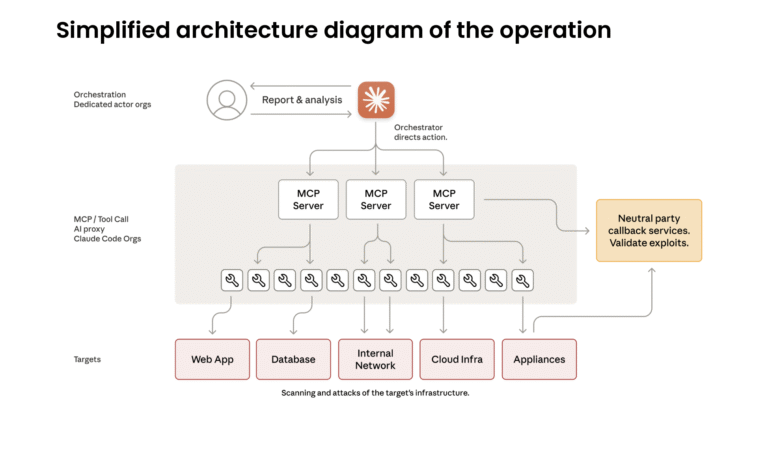
What Anthropic’s Latest Threat Intelligence Report Actually Reveals About AI Misuse, and What It Means for Enterprise AI Governance
Dario just released a We Must Pace the Frontier piece today: https://darioamodei.com/post/we-must-pace-the-frontier and this is on the tail of the intelligence layer…
 GOVERNANCE RISK AND COMPLIANCE
NYDFS Does Not Want Your Annual PDF. It Wants the Decision Trail.
The Department’s September 10 industry letter creates no new Part 500 duties.
Healthcare AI Does Not Have a Governance Gap. It Has a Jurisdiction Problem.
Pharma can find a biological target in a week that used to take a quarter.
What Will California’s New AI Auditors Actually Test?
Sacramento just created the country’s first registry for AI auditors and a framework for independent verification organizations.
 COOKIES
Cookie Compliance Consulting: What a Managed Cookie Consent Service Should Actually Do
For many companies, cookie compliance starts with a familiar project: choose a consent platform, install a banner, categorize the cookies and move…
 COMPLIANCE
What Website Remediation Actually Requires After an Enforcement Action
Every major CCPA enforcement action of the last few years shares a pattern that gets less attention than the settlement number itself.