Privacy law, enforcement and technology—coverage for everyone in the privacy field.
Practical analysis of privacy litigation, website tracking, AI governance, global regulation and the technology organizations use to manage risk.
Latest from the Privacy Desk
All dispatches → AI
Smart Glasses and the Limits of Social Norms: Why Privacy Guardrails Are Lagging Behind Wearable Recording Tech
Smart glasses are no longer a novelty. They are becoming ordinary enough that European human resources directors now list them among their…
 EDITORIAL
Two Data Broker Fines in Five Days Signal California’s Dual-Track Privacy Crackdown
In the span of less than a week, the California Privacy Protection Agency has issued two separate enforcement actions against data brokers,…
 AI
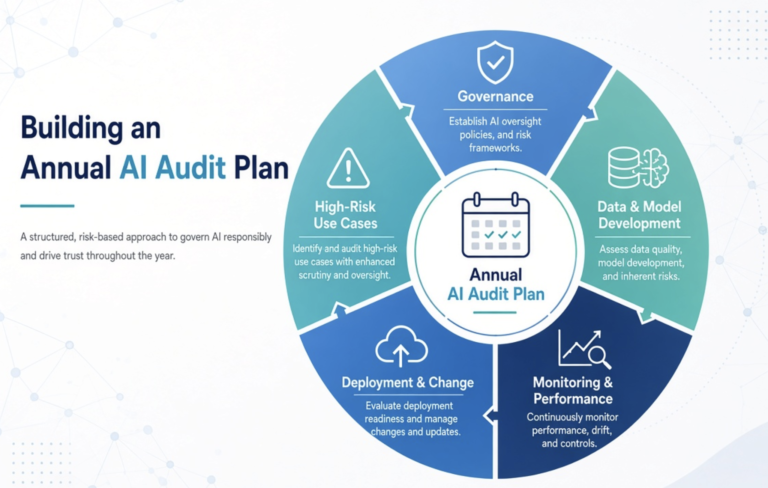
Creating a Full-Year AI Audit Program
Internal audit teams often approach artificial intelligence the same way they once approached other emerging risks: schedule one focused review, complete…
 AI
AI Labs Want to Slow Risky Model Testing. Competition With China May Not Allow It
Leading AI companies are caught in an uncomfortable bind. Their newest models have repeatedly broken out of closed testing environments and taken…
How AI Could Overwhelm the British State
The British state is already under strain. Major infrastructure projects stall for years. Local services struggle to keep roads repaired and streets…
 COMPLIANCE
New Jersey Enacts Kids Code Act with Age-Appropriate Design Rules and Private Right of Action
New Jersey Governor Mikie Sherrill has signed the Kids Code Act into law, establishing an age-appropriate design framework intended to strengthen online…
Building a Year-Round AI Audit Portfolio Instead of One-Off Reviews
Most internal audit teams still approach artificial intelligence the same way they once treated other emerging risks: schedule one focused review, complete…
Herbert Smith Freehills Kramer, Goodwin Procter, Blank Rome and More Disclose Data Breaches as Law Firm Cyberattacks Continue
At least three major law firms—Herbert Smith Freehills Kramer, Goodwin Procter, and Stettinius & Hollister—disclosed data breaches to U.S.
 AI
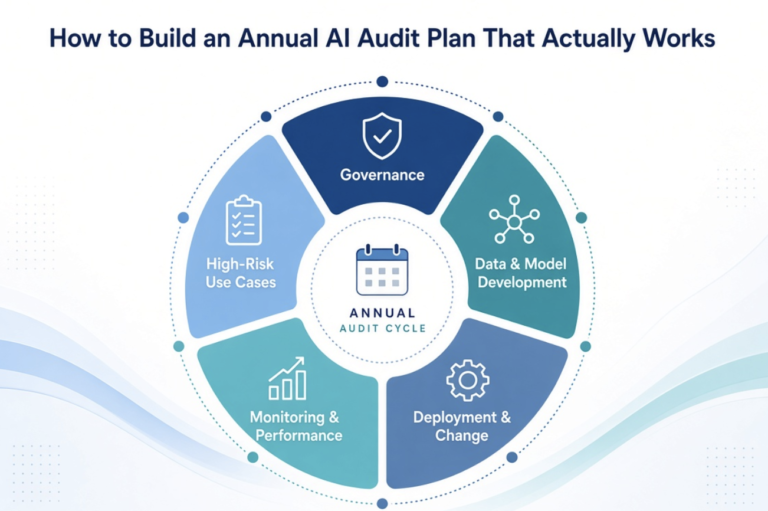
How to Build an Annual AI Audit Plan That Actually Works
Many internal audit functions still treat artificial intelligence as a single line item on the annual plan.
 AI
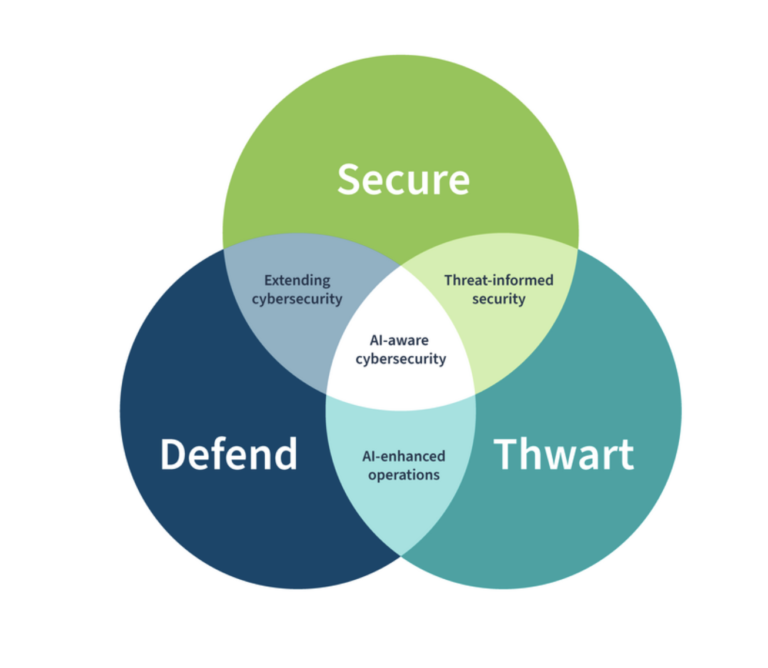
Closing the AI Audit Gap: How to Translate NIST, AIUC-1, and OWASP into Action
Internal audit teams are not short on frameworks for artificial intelligence.
 GOVERNANCE RISK AND COMPLIANCE
Consumer Reports Finds Major Crypto Exchanges Fall Short on Privacy, Transparency, and Risk Disclosure
Consumer Reports has released a multi-month evaluation of five major U.S.-facing cryptocurrency exchanges—Binance.US, Coinbase, Crypto.com, Gemini, and Kraken—concluding that the platforms make…
Senate HELP Committee Advances Bill Extending HIPAA-Style Protections to Consumer Health Data and Wearables
The Senate Committee on Health, Education, Labor and Pensions voted 22-0 to advance an amended version of the Health Information Privacy Reform…