Alex Proctor
Alex Proctor is a privacy and data protection professional with 15 years of experience spanning healthcare, critical infrastructure, and other highly regulated industries. With a strong foundation in cybersecurity, Alex brings a unique perspective to privacy and AI leadership. He led a cybersecurity consulting practice for half a decade and has led cybersecurity and privacy governance, risk, and compliance programs at a prominent EPC firm. He has also developed AI governance training resources used by cyber governance professionals globally. Alex serves as the Chief Trust & Privacy Officer at Captain Compliance—a privacy technology startup dedicated to simplifying complex privacy challenges and reducing privacy risk. The company’s streamlined platform addresses cookie consent management, dynamic privacy notices, data subject request processing, and more. Alex graduated from Oakland University with a bachelor’s degree in Management Information Systems (MIS). He holds numerous industry certifications, including the ISC2 CISSP and CCSP, as well as the IAPP CIPM, CIPP/E, CIPP/US, CIPT, and AIGP. Recognized by the IAPP as a Fellow of Information Privacy (FIP), Alex also chairs the IAPP Detroit KnowledgeNet chapter. He fosters dialogue and knowledge-sharing within the privacy community.
Posted articles 105 TOTAL
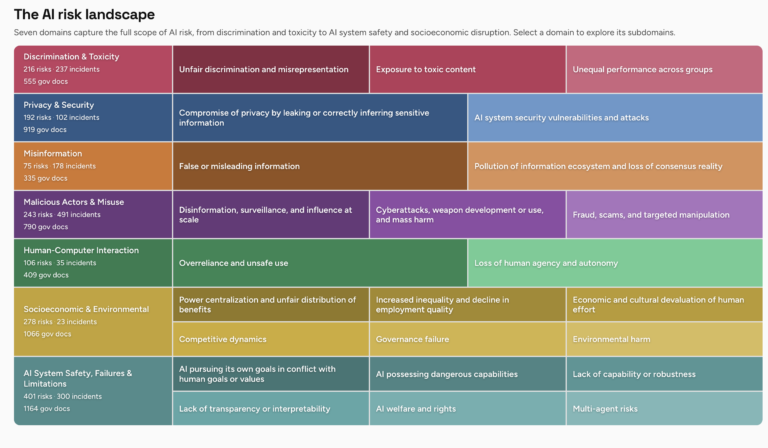
Why Transparent AI-Era Privacy Notices Matter for Consumer Education
Artificial intelligence quietly is starting to power everything from personalized recommendations to autonomous decision-making, clear communication about data practices isn’t just a…
 AI
Gartner Says AI Governance Comes Before AI Hype
AI is moving faster than most organizations can govern it. That is the real warning behind Gartner’s latest comments on artificial intelligence.…
 AI
AI Inventory: The First Step in AI Governance
Most companies do not have an AI governance problem because they built one powerful artificial intelligence system.
NIST AI Risk Management Framework
The NIST AI Risk Management Framework launched in January 2023 with language so carefully neutral it could have been written by committee…
DATA Data Embassies vs. Data Corridors: A Compliance Officer’s Guide to the Cross-Border Data Transfer Framework
Data embassies are one of the most discussed — and most misunderstood — concepts in global data governance.
 AI
AI Governance Framework: How to Align with the EU AI Act, NIST AI RMF, and State AI Laws
Artificial intelligence is already inside your business. It may not be approved. It may not be documented. It may not be reviewed…
Ransomware Criminals Evolve: Rapid7 CTO Reveals Shift to Data Theft, Extortion, and Vulnerability Exploitation
In the relentless cat-and-mouse game between cybercriminals and defenders, ransomware operators are proving once again why they remain one of the most…
 AI
GDPR Compliance When Using Claude Enterprise
A question spreading across compliance forums right now cuts straight to the heart of how modern businesses are deploying AI tools: if…
 AI
White House and Congress Revive Push to Block State AI Laws
The federal fight over artificial intelligence regulation is back.
New York Just Voted to Ban Surveillance Pricing. Every Other State Should Be Watching
A price should be universal. You walk into a store, you see a number, and that number is the same number your…
Charter Cyberattack Exposes 4.9 Million Accounts as Employee Credential Attacks Hit Major Companies
Charter Communications, the telecommunications company behind the Spectrum brand, has confirmed a cyberattack that exposed personal information tied to millions of accounts,…
 AI
AI Connectors, Insider Risk and the Data Flows Nobody Is Mapping
Most privacy programs are built on a foundational assumption: data flows are known, mapped and controlled.
Check your own site
See what your website is actually sending.
Run a free privacy audit and find the cookies, pixels, session-replay tools, and trackers running right now — plus the ones that commonly show up in privacy claims. A real review of your site, not just a scan.