Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
Boards love a clean penetration test report. Attackers do not care about one. That gap is what the UK’s National Cyber Security Centre is trying to close with its new Cyber Adversary Simulation scheme, launched on November 11, 2026. The scheme assures commercial providers of red-team style testing against an NCSC standard, so that organisations, and the regulators and government departments that oversee them, can buy realistic attack simulations with some confidence in the quality. For banks, insurers, critical infrastructure operators and anyone else who has to prove resilience rather than just claim it, the scheme also raises a practical question: what kind of testing evidence will an oversight body actually find persuasive?
TL;DR
- The NCSC launched its Cyber Adversary Simulation (CyAS) scheme on November 11, 2026, assuring commercial red-team providers against an NCSC-defined standard and starting as a minimum viable product.
- CyAS is capability-led: assured testers run their own reconnaissance and build customer-specific attack plans instead of replaying purchased threat intelligence or documented attacker techniques.
- Separately, an October 27 NCSC blog explains how industry, the NCSC and the FCA worked on guidance about sharing cyber incident information without breaching UK market abuse rules.
What the NCSC launched
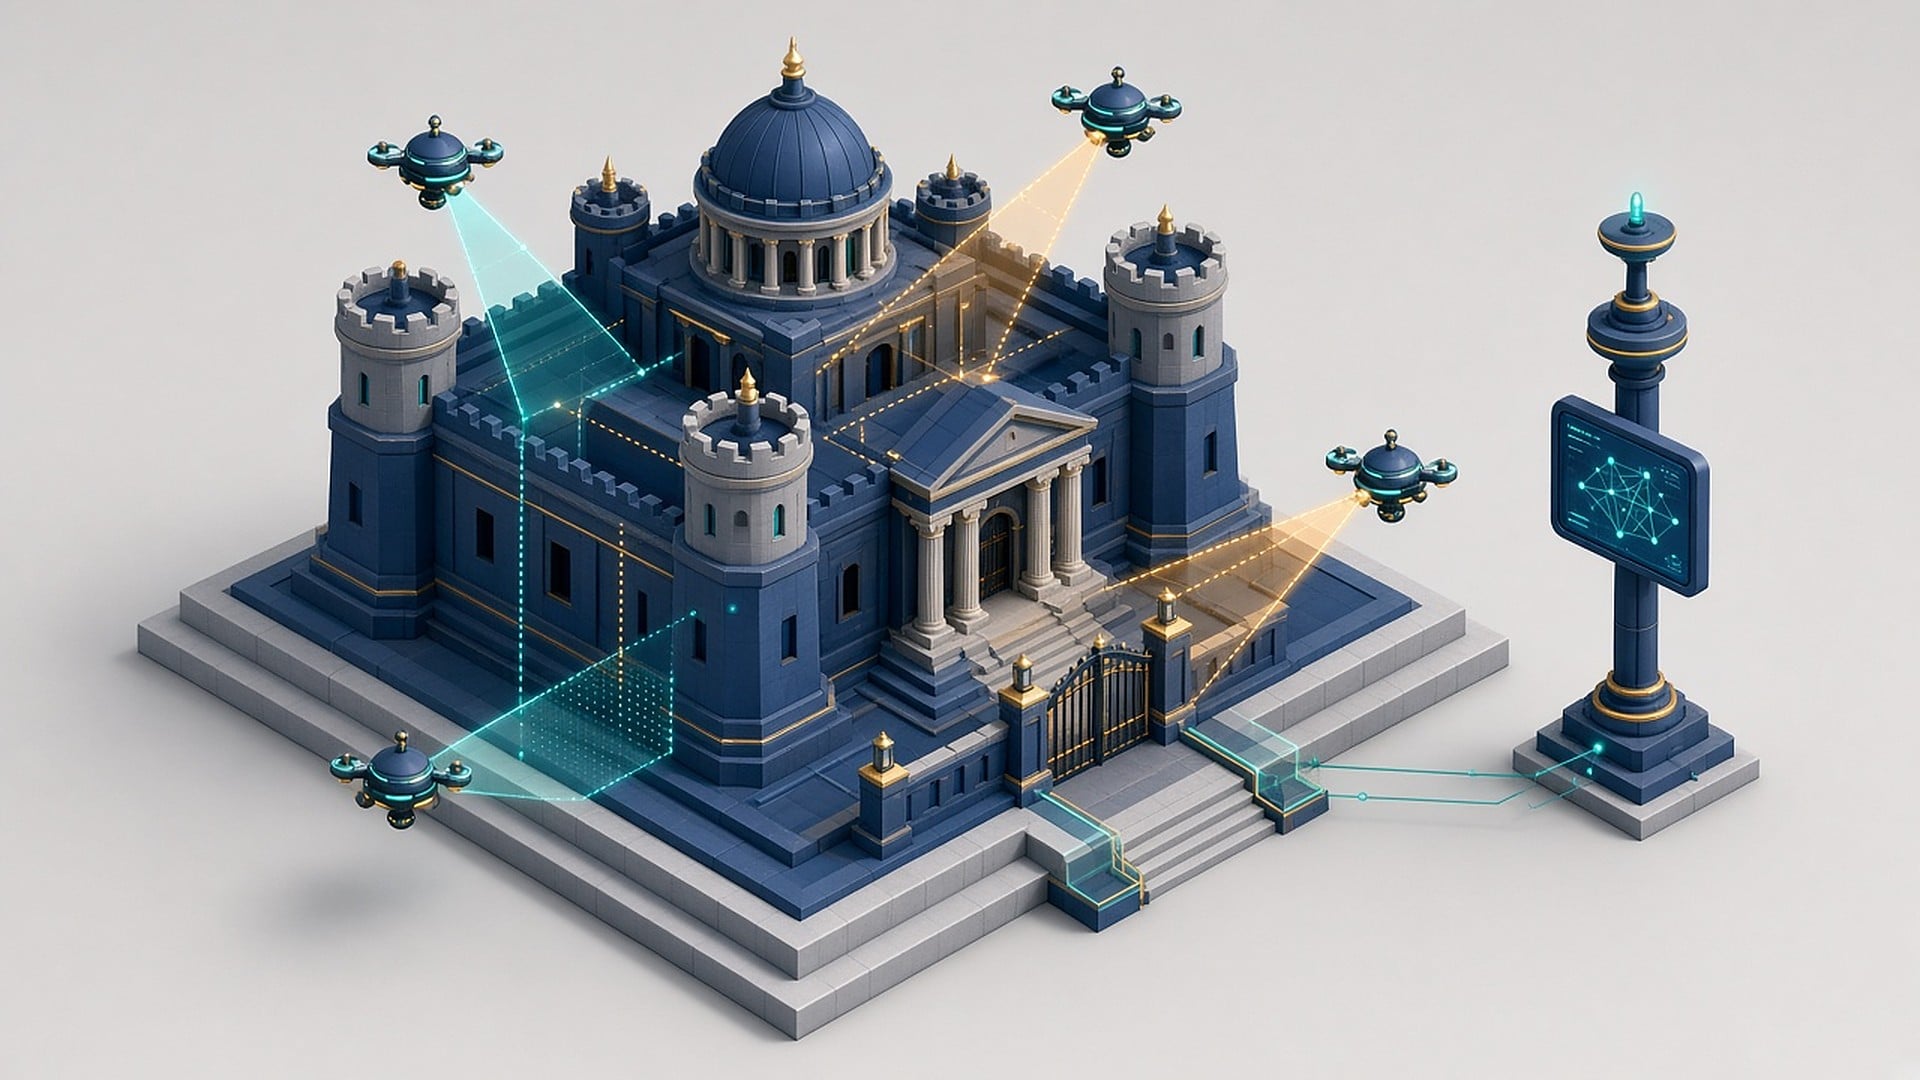
According to the NCSC’s launch announcement, CyAS is the latest of its Industry Assurance schemes. Commercial providers are assessed against an NCSC-defined standard, and buyers can pick from a published list of assured providers. The scheme was developed with what the NCSC calls Cyber Oversight Bodies, including regulators and Lead Government Departments, to create a common core standard while letting individual customers add their own requirements.
Two quotes capture the intent. Chief Technology Officer Ollie Whitehouse said: “You cannot improve what you do not know.” Deputy Director Chris Ensor described CyAS as “moving beyond traditional pen testing and auditing of controls.” The NCSC positions the scheme alongside the Cyber Assessment Framework (CAF) and its Cyber Resilience Audit scheme, and says together they give oversight bodies a trusted way to gather evidence of resilience across the sectors they supervise.
The scheme is starting small. It will operate initially as a minimum viable product while the NCSC tests demand and refines the methodology. The Scheme Standard and Working Practices Document were published in September, alongside new guidance for buyers.
A small correction to some early coverage: the NCSC abbreviates the scheme as CyAS, not CAS, which helps avoid confusion with the CAF.
How CyAS differs from a penetration test
The NCSC’s guidance, “Adversary simulation: what you need to know”, draws a sharp line. A penetration test tries to find as many technical vulnerabilities as possible, usually with detailed information supplied by the client. Adversary simulation tests whether defences and detection actually work against a realistic attacker pursuing agreed objectives, and the customer shares only the minimum, such as a primary domain name.
The NCSC’s version is also “capability-led.” Rather than replaying a script based on commercially procured threat intelligence or known tactics, techniques and procedures, assured testers do their own reconnaissance and apply an adversarial mindset. The guidance argues that published techniques are “inherently retrospective” and may not reflect current tradecraft. Other features stand out:
- Two starting points. A full spectrum engagement starts outside the network and tries to breach the perimeter; an assumed breach engagement starts from a foothold inside.
- Realistic duration. Typical engagements run 8 to 12 weeks, and full spectrum work around 16 weeks.
- De-chaining. If testers stall at the perimeter, the customer can hand them a low-privilege account so testing continues, which also shows what a malicious insider or compromised trusted third party could achieve.
- Different reports. Reports explain how objectives were reached and where detection opportunities were missed, and every CyAS report must map findings to the CAF.
The guidance is candid that this is not for everyone. Adversary simulation suits organisations that already assess risks, have established defences and run robust monitoring. Less mature organisations are pointed to Cyber Essentials, Cyber Advisors, CHECK penetration testing, Cyber Incident Exercising and other NCSC services.
Where CyAS fits for regulated financial firms
UK financial firms already know threat-led testing through CBEST, which the Bank of England, the PRA and the FCA have used as a supervisory tool since 2014. CBEST is threat intelligence-led and run within a regulator-driven framework. In the EU, the Digital Operational Resilience Act requires threat-led penetration testing (TLPT) for designated financial entities, with technical standards in Delegated Regulation (EU) 2025/1190, which entered into force on July 8, 2025.
The NCSC has not said how CyAS will interact with CBEST or DORA TLPT, so firms should not assume a CyAS engagement substitutes for a regulator-mandated test. The methodologies also differ in emphasis: CBEST and TLPT start from threat intelligence, while CyAS deliberately does not depend on purchased intelligence. For a UK firm, CyAS looks most useful between formal regulatory tests, for business lines outside a CBEST scope, or as evidence for operational resilience self-assessments under the UK impact tolerance regime.
Supervisors increasingly want evidence of outcomes, not attestations, a theme familiar from cases such as the S-Pankki mobile app security fine and from incidents like the Lloyds Bank IT glitch. The assurance industry has also had its credibility tested, as the Delve scandal over fake SOC 2 audits showed. An NCSC-assured provider list gives buyers one more way to check that a red team is what it says it is.
What the FCA blog actually covered
The second item often bundled with the CyAS launch is a blog by NCSC Senior Resilience Lead Mark K, published October 27, 2026. It is not about red teaming. It describes how industry, the NCSC and the FCA tackled a specific worry: listed companies were unsure whether sharing cyber incident details with the NCSC or trusted information-sharing communities could breach the UK Market Abuse Regulation, because those details might be inside information.
The result was FCA guidance on disclosing inside information relating to cyber incidents. The blog says sharing with the NCSC may be compatible with regulatory obligations because it can be consistent with acting in the normal exercise of employment, profession or duties, and that the guidance also recognises NCSC-led sharing communities. Organisations still have to assess their own circumstances. The NCSC blog states that “collaboration between industry, regulators and cyber security experts can help turn uncertainty into practical guidance.”
A practical playbook for commissioning adversary simulation
- Check your maturity first. If you cannot yet detect and triage an intrusion, spend the budget on monitoring and incident response before red teaming.
- Define objectives around critical functions. The NCSC puts the onus on the customer to name the essential functions whose compromise would be most damaging.
- Treat the tester as a high-risk supplier. A red team will hold credentials, reconnaissance data and possibly employee personal data. Apply the same third-party risk management practices you would to any privileged vendor: contracts, data handling terms, confidentiality and deletion on exit.
- Agree escalation and safety rules in writing. The guidance expects pre-agreed options if defenders detect the attack, and tooling with guardrails to protect live systems.
- Protect people in social engineering. The NCSC says reports should anonymise targeted users and focus on privileges gained, which also helps with data protection.
- Plan for third-party paths. Use de-chaining to test what a compromised supplier account could reach, a blind spot even mature TPRM programmes can miss.
- Close the loop. Track remediation against the CAF mapping and keep the contemporaneous activity record the guidance requires, so you can show a supervisor what was tested and fixed.
For a broader view of how AI is changing attacker capability, our AI cyberattack compliance playbook covers the legal side.
FAQ
Is using a CyAS-assured provider mandatory?
No. The NCSC presents CyAS as an assurance scheme to help buyers choose providers. Any requirement to use one would have to come from a regulator, contract or government policy.
Does a CyAS engagement replace CBEST or DORA TLPT?
The NCSC has not said so. Treat CyAS as complementary unless your supervisor confirms otherwise.
How long should we budget for?
The NCSC says typical engagements take 8 to 12 weeks, with full spectrum engagements around 16 weeks.
Can we share incident details with the NCSC during a live incident if we are listed?
FCA guidance, as described by the NCSC, indicates such sharing may be compatible with market abuse obligations, but each organisation must assess its own position.
Evidence beats confidence
The most useful line in the NCSC’s material may be the simplest: you cannot improve what you do not know. A clean test report proves very little if the test was easy. CyAS gives organisations a way to buy hard tests from vetted providers, and gives supervisors a common yardstick. The firms that benefit most will be those willing to hear bad news early.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.