Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
Security teams have spent October 2026 patching around the clock, and people in the incident-response business have started calling it “Black October.” The Wall Street Journal reported on October 23 that attackers ranging from state-backed groups to small-time criminals are using AI agents and automated hacking frameworks to break in faster, sort stolen data at scale and write exploit code within hours of a flaw going public. For legal and compliance teams, this is more than a technical story. Faster attacks shorten the time for every decision they own, from contract rights against vendors to what a company tells regulators and investors. This guide sets out what is verified so far and the practical steps that belong on counsel’s desk this quarter.
TL;DR
- The Wall Street Journal reported in late October 2026 on a surge of AI-assisted cyberattacks, and Microsoft documented a China-aligned group, Storm-0940, using the open-source agentic framework ARTEX against hundreds of organizations.
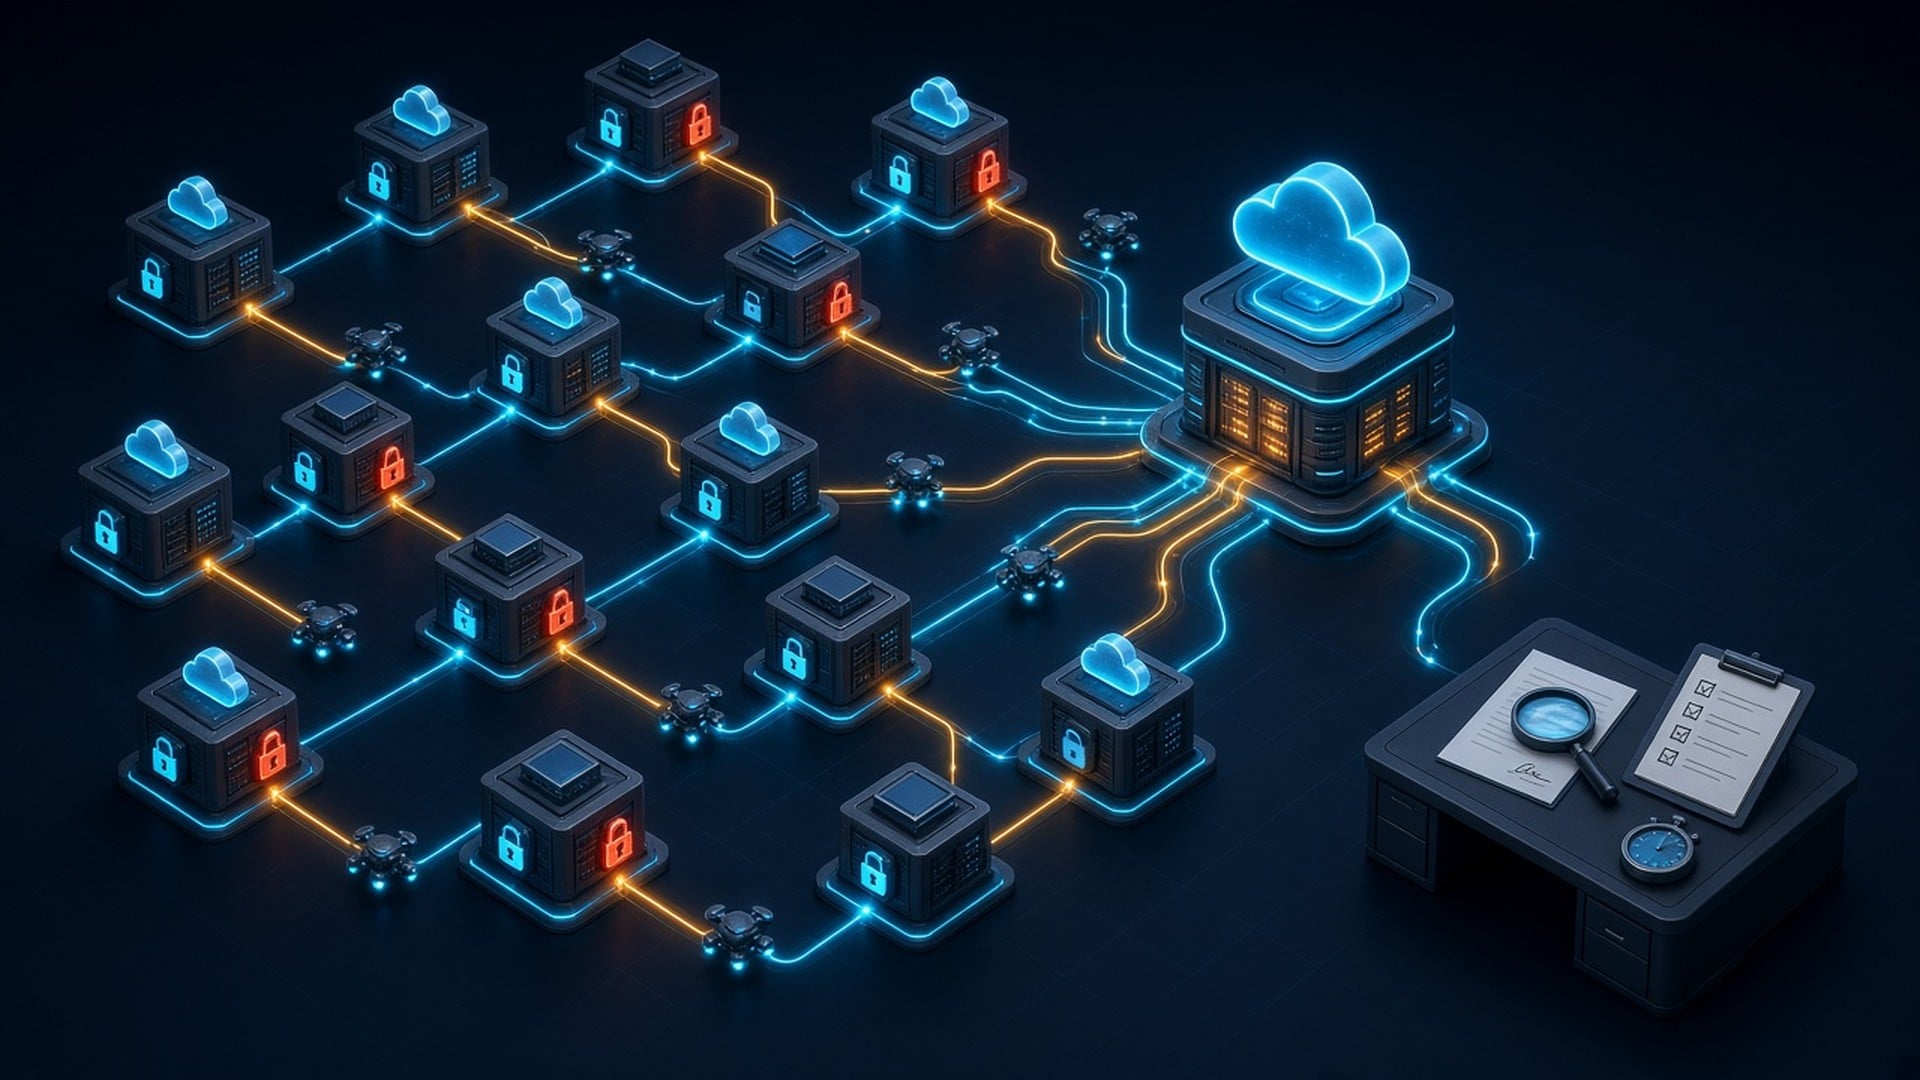
- In that campaign, attackers abused a trusted third-party cloud backup application to reach customer Microsoft 365 environments, in some cases going from first targeting to privileged access in under three hours.
- Legal and compliance teams should brief leadership on the new speed of attacks, review technology vendor contracts for notice and cooperation duties, and check incident facts carefully before any public or regulatory disclosure.
What is actually confirmed about the October wave
The Journal’s reporting, by Robert McMillan, rests on named sources. Adam Meyers, a senior vice president at CrowdStrike, described “an explosion of these agentic adversaries” used by advanced and unsophisticated attackers alike. Steven Adair, president of Volexity, said he expects “a massive number of compromise disclosures in the coming weeks and months.” Sherri Davidoff of LMG Security said that a year ago almost none of the incident responders she polls saw signs of AI use, and that last quarter it had become routine. The paper also reported that U.S. agencies told some organizations unable to patch a set of newly disclosed web flaws quickly to take their sites offline. That detail comes from the Journal’s account and we have not seen the underlying government notice.
The most detailed primary source is Microsoft’s own write-up, published October 21. Microsoft says that as early as September 2026, Storm-0940, a China-state-aligned actor active since 2021, used ARTEX, an open-source multi-agent penetration testing framework, to automate attacks against hundreds of organizations in sectors including financial services, government, legal, manufacturing and technology. Microsoft assesses that the same group was behind the ConnectWise cloud backup supply chain compromise disclosed in mid-October. After gaining control of identities belonging to ConnectWise cloud applications, the actor’s agents used that trusted access to authenticate to customer tenants. Microsoft says ARTEX was used to attempt sign-ins to more than 2,250 tenants, and that in some environments the agents went on to reconnaissance, application credential changes and privilege modifications.
Two caveats from Microsoft matter for lawyers. First, it says the activity did not result from a compromise of or vulnerability in Microsoft’s own systems. Second, it says the presence of an affected application, or even a successful authentication, “does not necessarily indicate” that customer data was accessed or exfiltrated. That distinction between exposure and confirmed access shapes every notification decision that follows.
Governments are taking the trend seriously. Canada’s Centre for Cyber Security issued a bulletin warning that agentic AI is accelerating cyber attacks. It describes the significance of the campaign as “the emergence of a reusable framework that can help conduct cyber operations on an industrial scale,” and says humans still pick targets and objectives while more of the work in between is handed to machines. Earlier in October, attackers also used ARTEX in breaches of South Korean financial institutions, which we covered in our look at AI-assisted bank hacks by amateur attackers.
Why speed is a legal problem, not only a security one
Most corporate incident plans assume a human-paced attacker. Escalation trees, board notification thresholds and outside-counsel engagement steps were written for intrusions that unfold over days or weeks. Microsoft’s three-hour figure, and the Canadian bulletin’s warning that decisions “may soon have to be made within minutes,” undercut that assumption. If the people who can authorize disabling a critical vendor integration are not reachable on a Saturday night, the plan is already out of date.
The second shift is volume. Agentic tools try many entry points at once and generate large amounts of log data. That helps forensic teams later, but it also means early indicators will be noisy and often wrong. Pressure to say something publicly will arrive before the facts are settled.
Three steps for legal and compliance teams now
- Brief senior leadership on AI-enabled attacks, in plain terms. A short session for the executive team and the board’s risk or audit committee should cover what changed (speed, scale and the abuse of trusted integrations), what the company’s exposure looks like, and which decisions may need to be taken out of hours. Put names next to those decisions: who can cut off a vendor connection, who can approve taking a website offline, who decides on regulator outreach. Boards that oversee cyber risk directly will expect this, and lapses at the top are a recurring theme in cases where privacy failures start with leadership.
- Review technology vendor contracts with the ConnectWise pattern in mind. The October campaign moved through a multi-tenant application that customers had already granted broad permissions. That makes contract terms as important as firewall rules. A focused review should check:
- How quickly the vendor must notify you of a security incident, and whether “incident” covers attempted or suspected compromise rather than only confirmed data loss.
- Whether the vendor must preserve logs and share forensic findings, indicators of compromise and containment guidance, and on what timeline.
- What permissions and OAuth scopes the integration holds, and whether the contract requires least-privilege access and lets you audit it.
- Cooperation duties for regulatory notifications, plus indemnity and liability caps that match the data the vendor can reach.
- Sub-processor and AI-tool use by the vendor itself, including whether it relies on agentic tooling with access to your environment.
A structured third-party risk management program makes this repeatable, and the questions belong in vendor due diligence for new contracts as well as renewals.
- Fact-check the incident before you disclose it. Accuracy now carries more weight than speed alone. Before a press statement, customer notice or regulatory filing, counsel should test each sentence against the forensic record: was data accessed, or was an application merely present? Which systems, which time window, which data categories? Avoid early statements such as “no customer data was affected” that the investigation has not yet supported. A disclosure that has to be corrected later can create more legal exposure than the incident.
Disclosure rules that set the clock
For U.S. public companies, the SEC’s 2023 cybersecurity rule remains in force. Form 8-K Item 1.05 requires disclosure within four business days after the company determines an incident is material, and the materiality determination itself must be made without unreasonable delay after discovery. A delay is available only if the U.S. Attorney General finds that disclosure poses a substantial risk to national security or public safety. SEC staff have also said companies can use Item 8.01 to report incidents they have not yet judged material, which avoids the confusion of filing under 1.05 too early. Business groups petitioned the SEC in 2025 to rescind Item 1.05, but no rescission has been adopted.
Privately held companies face their own clocks: state breach notification laws, sector rules for banks, insurers and health entities, and contract terms with customers that may be shorter than any statute. In Europe, GDPR’s 72-hour regulator notice still runs from awareness of a personal data breach. Each of these depends on the same question the Microsoft guidance raises: what does the evidence actually show was accessed?
The pattern is not new. In April 2026, Vercel traced an intrusion to a compromised third-party AI tool and an over-permissioned OAuth grant. What October adds is machine speed: the same kind of trusted-integration abuse, attempted against thousands of tenants at once.
Practical containment points to align with security
Microsoft’s mitigation list includes advice that legal teams should support rather than override. It warns against deleting affected enterprise applications as a first response, and tells customers to preserve sign-in, audit and Graph telemetry before making irreversible changes. That lines up with litigation-hold duties. Counsel should confirm that legal hold notices cover cloud audit logs and vendor-held records, and that outside forensic firms are engaged in a way that protects privilege where possible.
Frequently asked questions
Is “Black October” an official designation?
No. It is an informal label that people in the security field have been using, as reported by the Wall Street Journal. It describes a cluster of AI-assisted attacks and urgent patching in October 2026, not a single incident.
If our tenant had the affected vendor app installed, were we breached?
Not necessarily. Microsoft says the presence of an affected application, or even a successful sign-in, does not by itself show that data was accessed. Investigation of sign-in and audit records is needed before reaching a conclusion.
Do we need a new incident response plan for AI attacks?
Usually not a new plan, but an updated one: shorter escalation paths, named out-of-hours decision makers, vendor-specific playbooks for high-privilege integrations, and a disclosure review step built into the timeline.
Should vendor questionnaires ask about AI?
Yes. Ask whether the vendor uses AI agents with access to customer systems, how those agents are governed, and how quickly the vendor will notify you of suspected compromise of its own cloud identities.
Counsel’s window is getting shorter
Agentic attack tools do not change what the law requires. They change how much time a company has to meet those requirements. The companies that handle the next wave well will have made three decisions in advance: who acts when an attack moves at machine speed, what their vendors owe them when trusted access is abused, and how every public statement gets checked against the evidence. Microsoft’s Storm-0940 analysis and the Canadian Centre for Cyber Security’s bulletin on agentic AI are useful starting points for that leadership briefing.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.