Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
India has switched on the first piece of its consent infrastructure. On 13 November 2026, exactly one year after the Digital Personal Data Protection Rules, 2025 were notified, the provisions governing the registration of consent managers came into force, and the Ministry of Electronics and Information Technology (MeitY) opened an online portal at dpbi.gov.in for companies that want to apply. The body that must approve those applications, the Data Protection Board of India, still had no chairperson or members when the portal went live. For privacy teams, the launch is less about an immediate legal duty and more about planning: it shows how consent will be managed in India from May 2027, and it raises practical questions about whether to plug into these new intermediaries at all.
TL;DR
- Section 6(9) of the DPDP Act and Rule 4 of the DPDP Rules, which require consent managers to register with the Data Protection Board, took effect on 13 November 2026, and MeitY launched the dpbi.gov.in application portal alongside them.
- Applicants must be companies incorporated in India with a net worth of at least ₹2 crore (about INR 20 million), measured as assets minus liabilities, plus independent certification of their platform and strict conflict-of-interest safeguards.
- Using a consent manager is optional for businesses, and the core duties of data fiduciaries, including notice, consent and grievance handling, start on 13 May 2027.
What actually changed on 13 November
India’s data protection law is being switched on in three stages. A commencement notification issued on 13 November 2025 brought the definitions and the provisions setting up the Data Protection Board into force straight away. It set a one-year delay for two provisions: Section 6(9), which says every consent manager must be registered with the Board, and Section 27(1)(d), which lets the Board inquire into a breach of any condition of registration and impose a penalty. Everything else, including the duties of businesses, the rights of individuals and most of the Board’s enforcement powers, follows on 13 May 2027.
The DPDP Rules, 2025 (G.S.R. 846(E)) follow the same timetable. Rule 1(3) says Rule 4, the consent manager rule, comes into force one year after publication. That is the provision that now applies, together with the First Schedule that sets out who can register and what a registered consent manager must do.
According to a Press Information Bureau release dated 14 November 2026, MeitY Secretary S. Krishnan launched the portal so that eligible companies can apply. The release says the Board will assess applications and that the list of registered consent managers will be published on the Board’s website. Business press, including Moneycontrol and The Hindu BusinessLine, reported that the Board was still not functional because its chairperson and members had not been appointed, and that a government official said appointments would come “soon.” The Board itself was established by a separate notification on 13 November 2025, so the institution exists on paper. What is missing is the people who would sign off on a registration.
What a consent manager is under Indian law
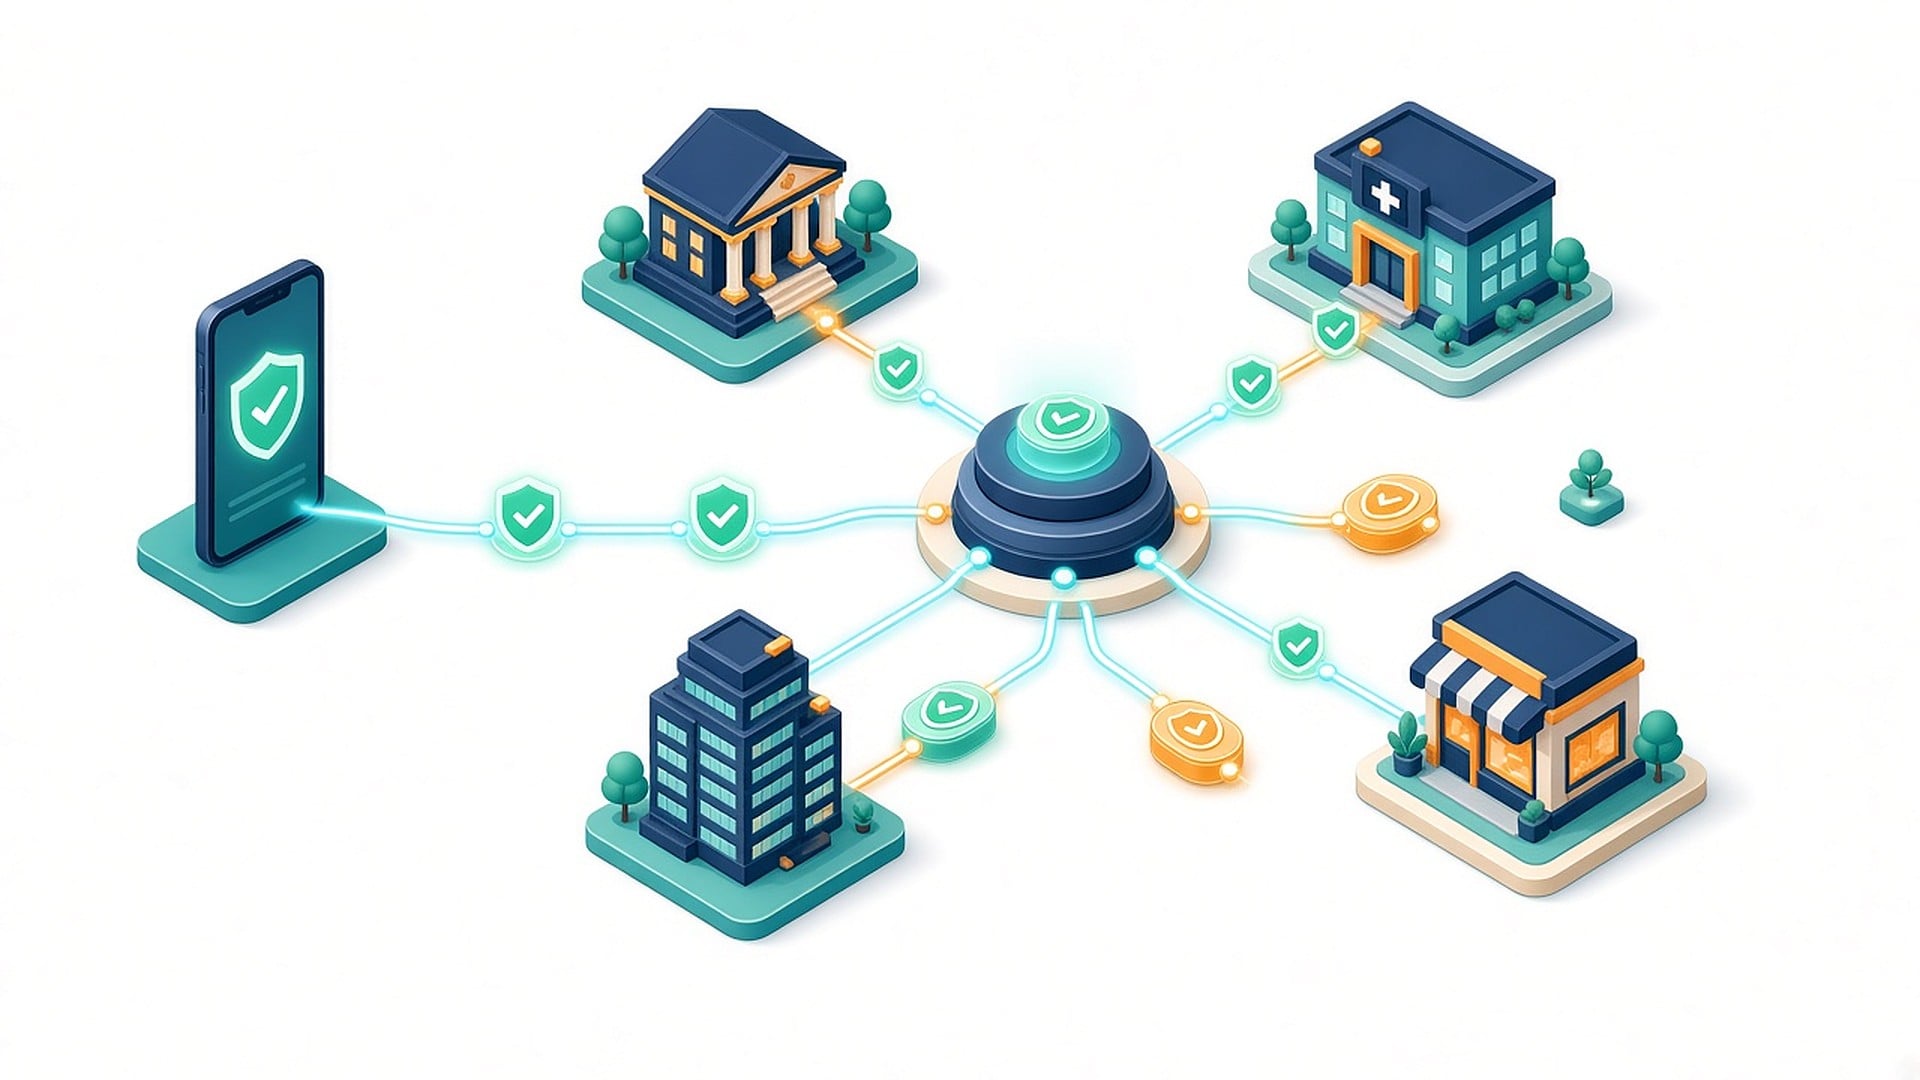
Section 2(g) of the Digital Personal Data Protection Act, 2023 defines a consent manager as a person registered with the Board who acts as a single point of contact so that a data principal can give, manage, review and withdraw consent through an accessible, transparent and interoperable platform. Section 6(7) lets an individual deal with a data fiduciary through such a platform, and Section 6(8) makes the consent manager accountable to the individual and requires it to act on her behalf.
That is a different idea from the consent management platform most companies run on their own websites. A CMP is a tool the business controls. An Indian consent manager is a regulated intermediary that works for the individual, sits between her and many businesses, and has a fiduciary duty to her. The policy goal, as Moneycontrol summarised it, is to reduce consent fatigue: instead of reading and answering a separate privacy notice on every site, a person could manage permissions in one place. That ambition responds to a widely shared concern that consent is under strain when people face hundreds of requests.
The Rules include an illustration that makes the model concrete. An individual is registered on a consent manager’s platform, and two banks are onboarded onto it. One bank asks for consent to process her account statement. She can grant it directly and share a statement she keeps in a digital locker, or she can route her consent through her own bank and instruct it to send the statement across. Readers familiar with India’s financial-sector account aggregator network will recognise the pattern.
Correcting the eligibility test
Some early summaries described the threshold as “global profits exceeding INR 20 million.” That is not what the Rules say. Item 4 of Part A of the First Schedule requires a net worth of not less than two crore rupees, and the note to the Schedule defines net worth as the total assets minus liabilities shown in the consent manager’s books of accounts. Two crore is 20 million rupees, so the figure is right, but it is a balance-sheet test on the Indian applicant, not a profit test and not a measure of a global group. The PIB release confirms the same ₹2 crore net worth floor.
The full list of registration conditions in Part A is broader than money:
- The applicant must be a company incorporated in India.
- It needs sufficient technical, operational and financial capacity, sound finances and management, and adequate business prospects and capital structure.
- Its directors, key managerial personnel and senior management must have a reputation for fairness and integrity.
- Its memorandum and articles of association must lock in the conflict-of-interest obligations, and those provisions can be amended only with the Board’s prior approval.
- Its proposed operations must be in the interests of data principals.
- It must be independently certified that its interoperable platform meets the data protection standards and assurance framework the Board publishes, and that its technical and organisational measures support them.
The last condition is a practical bottleneck. The certification refers to standards “as may be published by the Board,” and with no Board members in place, applicants and their advisers have pointed out that the technical and interoperability standards are not yet clear.
Obligations once registered
Part B of the First Schedule reads like a code of conduct for a neutral switchboard:
- Content blindness. Personal data shared through the platform must be made available in a way that the consent manager itself cannot read.
- Records. It must keep records of consents given, denied or withdrawn, the notices that accompanied each request, and any sharing of data with a recipient fiduciary, give the individual access, provide the record in machine-readable form on request, and keep it for at least seven years.
- Independence. It must avoid conflicts of interest with data fiduciaries, including through directors or managers holding directorships, financial interests, employment or ownership in them, and it must publish its promoters, directors, senior management and any shareholder above 2 percent.
- No outsourcing. It cannot sub-contract or assign its obligations, and control of the company cannot change hands without Board approval.
- Security and audit. It must take reasonable security safeguards and run audit mechanisms that report to the Board on controls, continued eligibility and compliance.
If a consent manager falls short, Rule 4 lets the Board direct it to fix the problem and, after a hearing, suspend or cancel its registration. The Act’s general penalty entry for breaches not listed elsewhere in its Schedule goes up to ₹50 crore, but the penalty machinery in Section 33 only comes into force on 13 May 2027.
What data fiduciaries should do now
Nothing in the November commencement creates a new duty for an ordinary business. Using a consent manager is a choice made by the individual and, in practice, by businesses that decide to be onboarded. Still, the window before May 2027 is the right time to decide how your consent stack will interact with these platforms.
- Map where you rely on consent in India. The Act leans heavily on consent, with a limited list of “legitimate uses” in Section 7. Identify every flow that depends on opt-in consent so you know which ones a consent manager could touch.
- Decide whether to onboard. Sectors that already exchange data between institutions, such as banking, lending and insurance, may see early demand. Consumer apps may wait until registered consent managers and standards actually exist.
- Make consent signals portable. A withdrawal received through a consent manager must stop processing just as quickly as one made on your own site. Review how you are orchestrating consent across systems so an external signal reaches every downstream processor.
- Align notices and records. Consent managers must store the notice that accompanied each request. Your Rule 3 notices, which apply from May 2027, should be itemised, standalone and in plain language, and your own records should be able to reconcile with an intermediary’s seven-year log.
- Update your user-facing controls. If you run a preference center, plan how it will show consents that came in through a third-party platform, so users do not see conflicting states.
- Watch the Board’s website. The registration particulars, the assurance framework and the list of registered consent managers will all be published there. Assign someone to track it.
How this compares with other regimes
The GDPR has no registered consent intermediary with a statutory duty to the individual, and US state laws rely mainly on opt-out mechanisms such as universal preference signals. India’s model is closer to a regulated utility layer. It also overlaps with technical work elsewhere on browser-level consent signals, which try to move consent choices out of individual banners. The difference is that India puts a licensed company, not a browser setting, at the centre.
Frequently asked questions
Can a foreign company register as a consent manager?
Not directly. Part A requires the applicant to be a company incorporated in India. A foreign group would need an Indian company that meets the net worth, management, certification and independence conditions on its own.
Can anyone be registered today?
Applications can be filed through the portal, but registration requires the Board to be satisfied that the conditions are met. As of the launch, the Board’s chairperson and members had not been appointed, so no approval timeline has been announced.
Do businesses have to work with consent managers?
No. The Act lets individuals use a consent manager; it does not oblige a data fiduciary to obtain all consent that way. A business that does onboard must honour consents and withdrawals received through the platform.
Can a consent manager read the data it helps share?
It should not be able to. Part B requires that data be made available or shared in a way that its contents are not readable by the consent manager, which pushes providers toward encrypted, pass-through designs.
A switchboard waiting for its operators
India has built the legal frame for a consent layer that no other major privacy regime has tried at this scale, and the application door is now open. What it lacks is a functioning regulator to approve applications and publish standards. Companies that use the next six months to make their consent records clean, portable and auditable will be ready whichever way that layer develops.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.