Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
Not every privacy theory is about secrecy. Some are about property. A recent Meta Pixel demand letter, and others like it sent to e-commerce and website operators, includes trespass to chattels as claim (d) and points to the _fbp cookie as the offending object. The idea is that placing a tracker on a visitor’s browser is like putting something on someone else’s goods without permission. The metaphor is easy to picture. Under California law, it has been a hard claim to keep alive unless the plaintiff can show that the device itself was impaired.
TL;DR
_fbpis a browser cookie associated with the Meta Pixel. Demand letters describe writing that cookie as a trespass to the visitor’s computer or phone.- The California Supreme Court held in Intel Corp. v. Hamidi that electronic contact is not trespass to chattels without actual impairment of the computer’s functioning.
- In Doe v. Tenet Healthcare, a federal court dismissed a cookie-based trespass claim because the plaintiffs did not allege a measurable decrease in storage, memory, or performance.
What trespass to chattels requires
Trespass to chattels is an old property tort. It covers intentional interference with another person’s personal property that causes actual harm, such as dispossession or impairment of the property’s condition, quality, or value. Courts have been cautious about extending it to unwanted electronic contacts that leave the machine working as before.
The leading California decision is Intel Corp. v. Hamidi, 30 Cal. 4th 1342 (2003). A former employee sent emails to thousands of Intel workers. Intel argued that the messages trespassed on its computer system. The California Supreme Court disagreed. Unwanted electronic communications, the court held, are not a trespass to chattels merely because they use someone’s system. The plaintiff must show that the system was impaired, for example by being slowed or taken out of service, not merely that the messages were unwelcome.
That impairment requirement is why cookie cases often fail at the pleading stage. A cookie is a small text file. Modern browsers are designed to store many of them. Unless the plaintiff can allege, in more than conclusory terms, that the particular cookie reduced storage, memory, battery life, or processing speed in a measurable way, Hamidi is an awkward fit.
How letters use the _fbp cookie
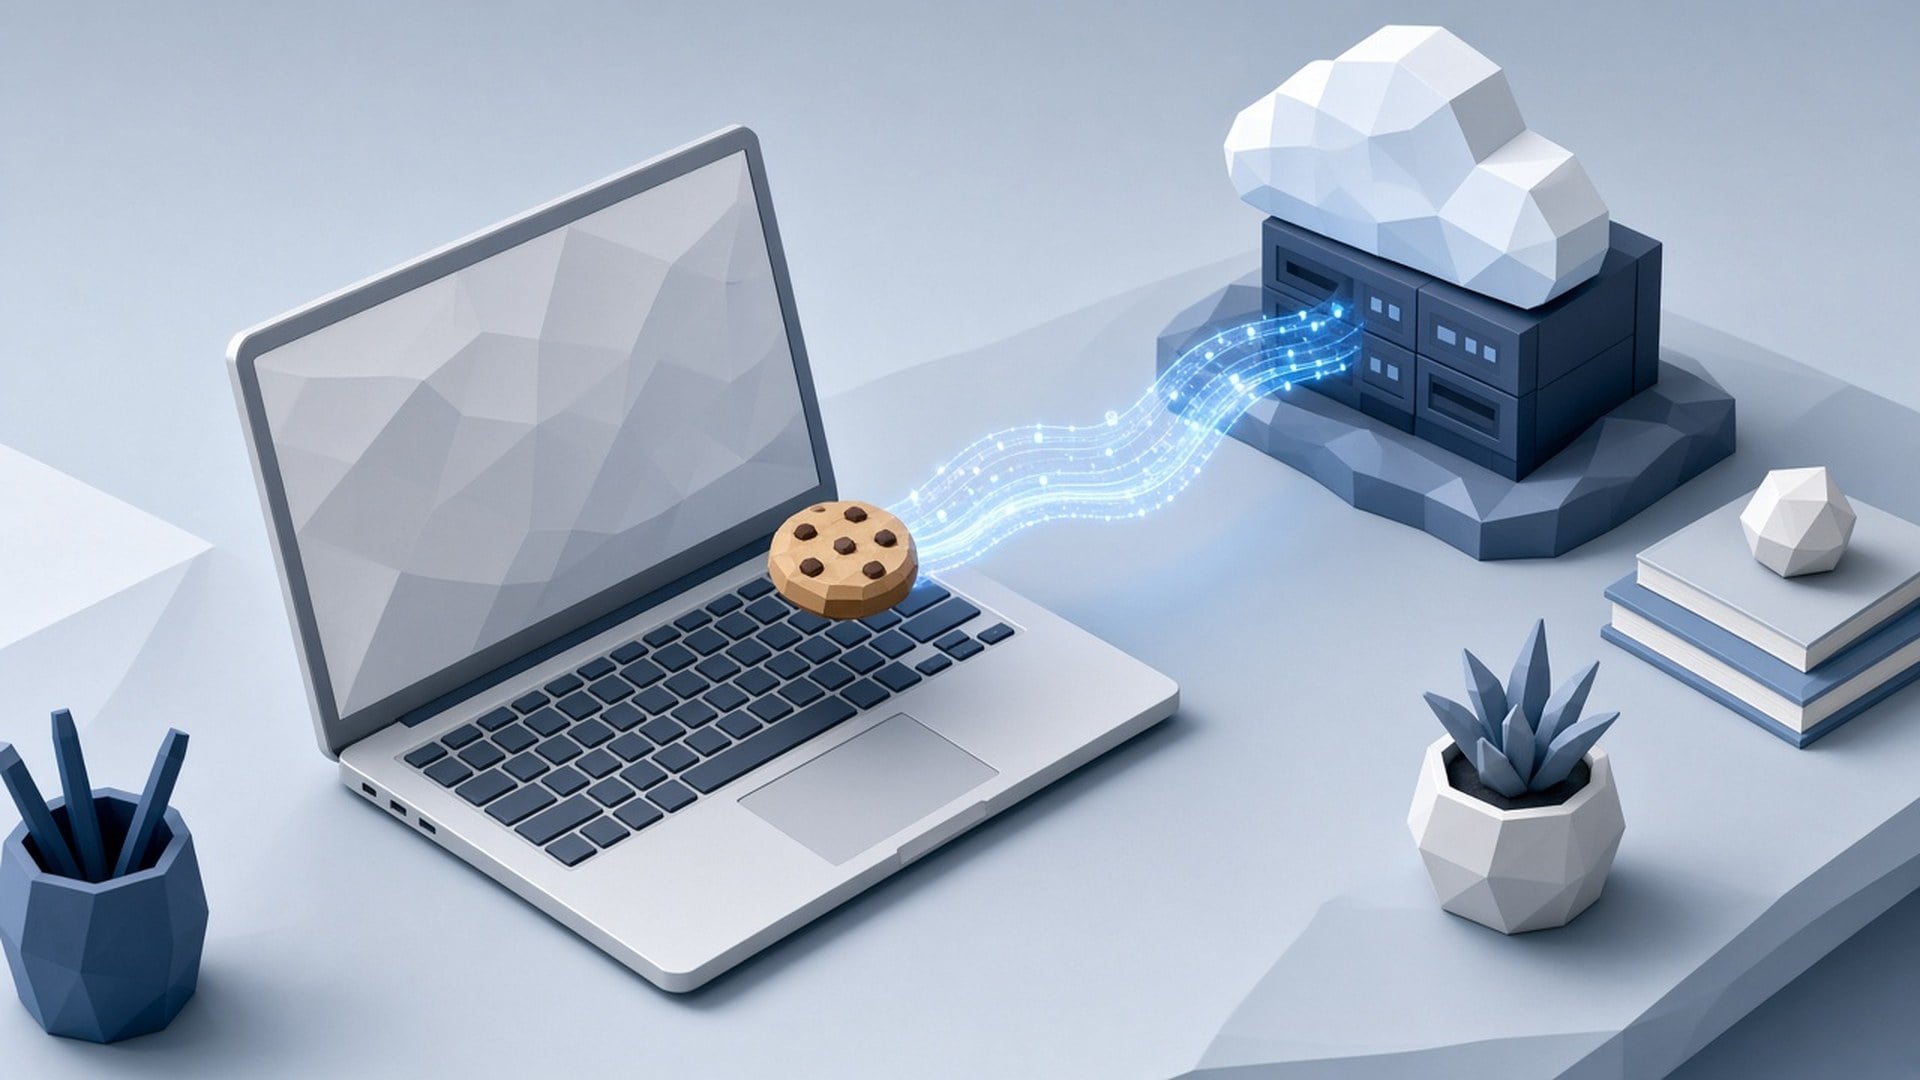
The Meta Pixel commonly sets a cookie named _fbp to help identify a browser over time. It sits alongside other identifiers and event data that the pixel can send to Meta. Plaintiff firms treat the write operation itself as the trespass: the business, by installing the pixel, caused code to place a file on the visitor’s device without permission and thereby interfered with the visitor’s possession of that device.
In the stacked letters we are seeing, this theory is not really about getting paid for a damaged laptop. It is another predicate in the ECPA crime-tort structure. If placing the cookie was a tort, the argument goes, then procuring Meta to intercept communications was done for a tortious purpose, and one-party consent should not apply. The cookie also gives counsel a tangible object to point to, which can feel more concrete than an abstract discussion of GET requests. Our explainer on how tracking pixels and cookies work together is useful background when a letter collapses the two into a single accusation.
The same letters often pair trespass with CDAFA claims under Penal Code section 502. Both theories talk about the visitor’s computer. They are still different claims. CDAFA is a computer-crime statute with a civil remedy and its own “without permission” and injury elements. Trespass is common law. Winning or losing one does not automatically decide the other, but courts that demand real device harm for trespass are often looking for a similar concreteness when they read CDAFA damage allegations.
What courts have done with cookie trespass theories
The most useful recent illustration is Doe v. Tenet Healthcare Corp., 789 F. Supp. 3d 814 (E.D. Cal. 2025), the same healthcare-pixel decision that letters cite for their ECPA theories. The court’s order dismissed the trespass claim. Plaintiffs had not alleged that the cookies caused a measurable decrease in storage, memory, or any other impairment of their devices. The court distinguished another pixel matter in which plaintiffs had at least alleged that cookies slowed their computers. That distinction is important. It shows both that some complaints try to plead around Hamidi and that judges are watching for more than the word “cookie.”
Even a slowdown allegation has to be made in good faith. A single advertising cookie is an implausible explanation for a sluggish phone, and courts can become skeptical of copy-and-paste impairment language. Demand letters that never mention speed, storage, or battery life are even thinner. They are relying on the idea that any unauthorized file is a trespass. Hamidi rejected that idea for electronic contacts that do not impair the system.
There is a separate conceptual problem when the business is the one who served the webpage the visitor requested. The visitor asked the site to send content. The site’s response included a script. Calling that exchange a trespass on the visitor’s machine starts to treat ordinary web functionality as a property tort. Judges have not been eager to go that far without a showing of harm.
Practical steps if trespass appears as claim (d)
- Find out whether
_fbpand related cookies are set before consent. The property story is weaker, and the rest of the letter is weaker, if marketing cookies wait for a choice. A cookie audit that tests scanning and GPC handling is the right starting point. - Do not invent a technical defense you cannot support. If the cookie does fire immediately, say so internally and fix it. Counsel can still argue Hamidi.
- Preserve browser and tag-manager evidence. If the dispute later turns on what files were written, you will want a snapshot of the site as it existed.
- Keep trespass in perspective when you evaluate settlement. This is usually among the weaker theories in the stack. It should not be ignored, because it is being used as a predicate, but it should not drive the number by itself.
How Captain Compliance addresses the underlying cookie
The operational issue is not whether a court will someday find that a 20-byte cookie damaged a laptop. It is whether your site writes advertising cookies before the visitor has made a choice you can document. Captain Compliance’s consent manager can prevent marketing tags, including the Meta Pixel, from running until that choice exists. The website scanner and Radar-powered cookie scan are designed to show whether _fbp and similar cookies still appear too early or ignore Global Privacy Control. That same control plane is what Compliance Shield is built around when it financially backs qualifying consent and disclosure claims on eligible, properly configured plans.
Frequently asked questions
Is every cookie a trespass?
No. California law looks for actual impairment of the chattel, not merely an unwanted file. A cookie your browser is designed to store, and that does not slow or damage the device, is a poor fit for the tort recognized in Hamidi.
Why do letters mention _fbp by name?
Because it is a concrete artifact associated with the Meta Pixel. Naming the cookie makes the property story easier to tell than talking only about JavaScript. The legal test still asks what harm that file caused.
If a healthcare case dismissed trespass, does that help an ordinary website?
It helps as persuasive authority that cookie placement without alleged device harm is not enough. It is not a binding judgment about your site. Plaintiffs may try to add slowdown allegations. The better response is still to stop writing advertising cookies before consent and to evaluate any remaining claim on the actual pleadings.
A cookie is not a broken machine
Trespass to chattels gives a demand letter something that feels physical: a file placed on someone else’s property. California’s highest court has already said that electronic contact without impairment is not that tort, and a 2025 federal order in a pixel case dismissed the claim for exactly that reason. Recipients should still understand why the cookie is in the letter. It is there to decorate the crime-tort exception and to make tracking sound like a break-in. The sounder reading is simpler. If the pixel is writing _fbp before any choice, fix the tag. If the letter alleges no harm to the device, treat claim (d) as one of the weaker boards in the stack, not as the one that holds the structure up.
This article is for educational purposes and is not legal advice.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.