Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
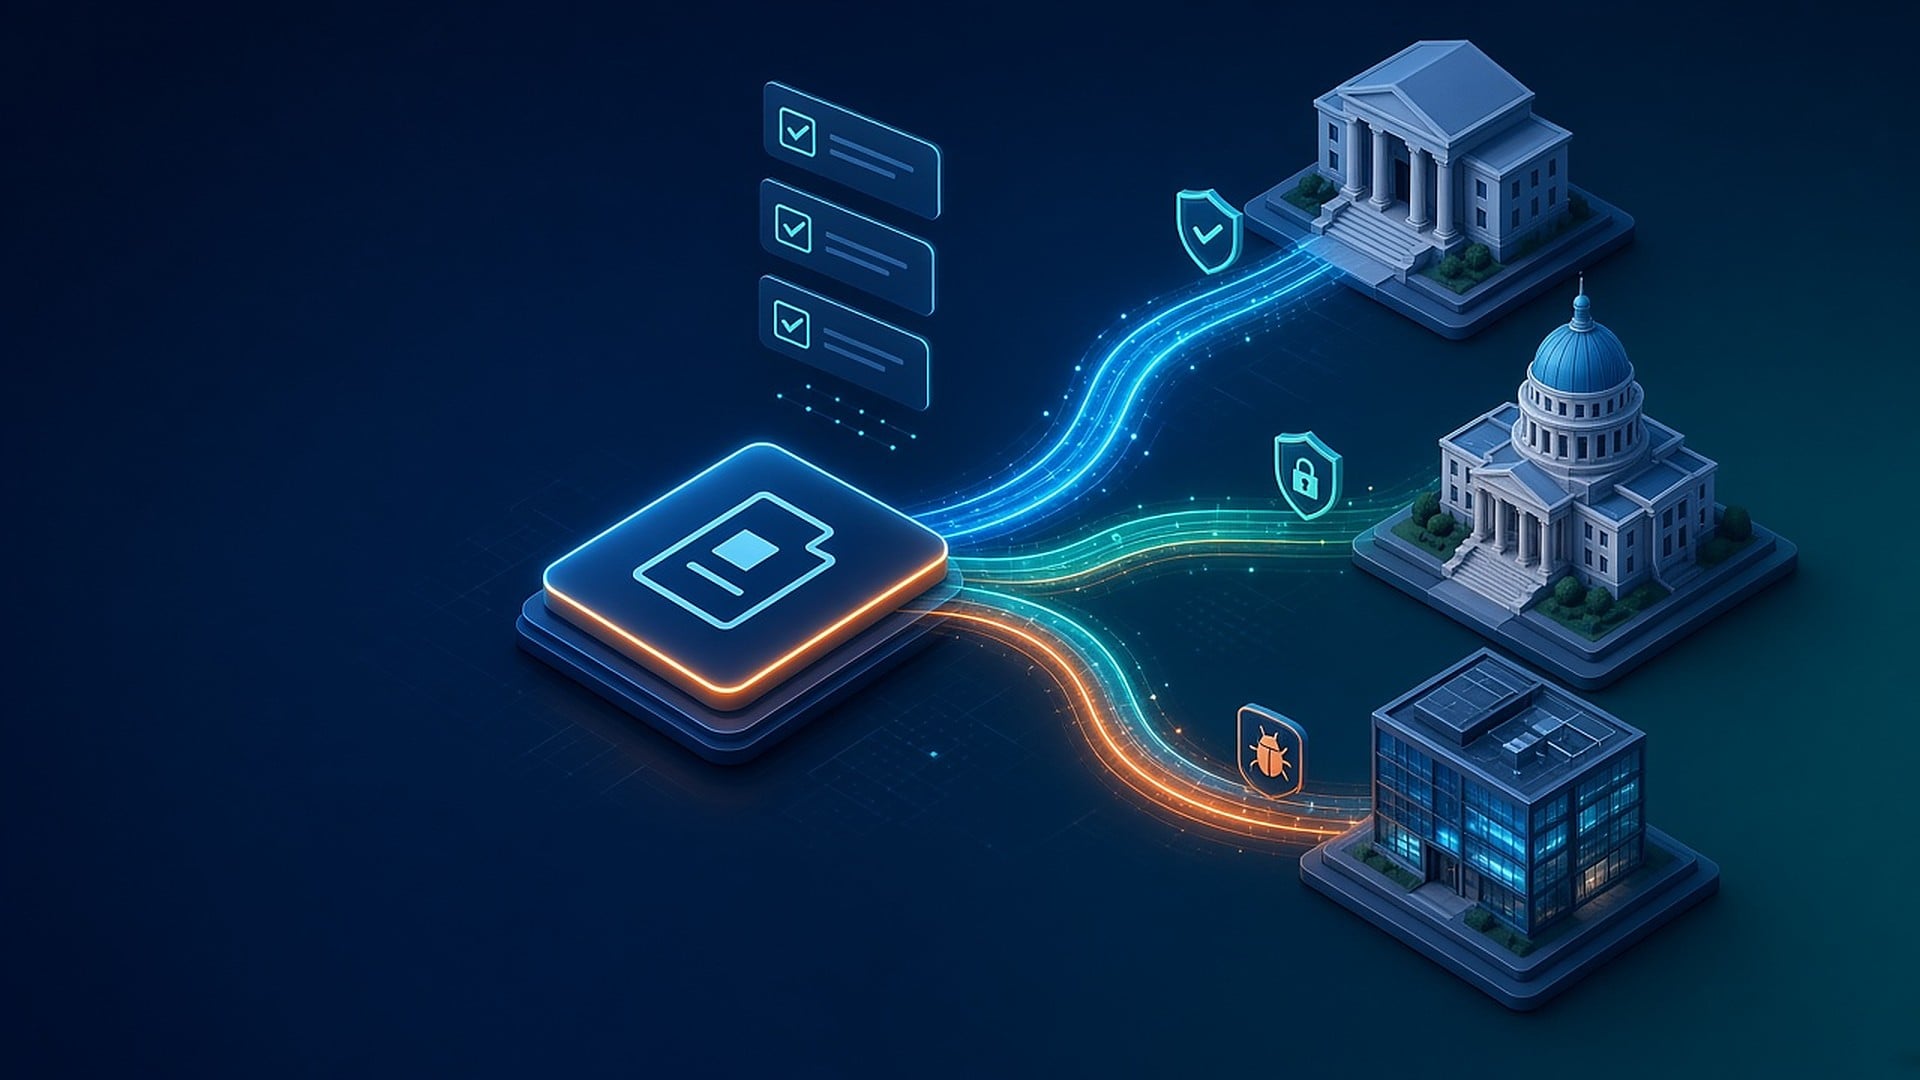
When a cyber incident hits, the same facts get typed into several forms by several people, often in different words. Security writes the CISA report. Privacy drafts the regulator notice. Legal handles the state attorney general letters. On November 9, 2026, the Cybersecurity and Infrastructure Security Agency released an updated cyber incident reporting form that asks for more detail in more standardised terms, including MITRE ATT&CK techniques. It is a good moment to stop writing the same incident three times. Organisations can build one internal intake record that feeds CISA, state breach notices and GDPR-style notifications from a single set of verified facts.
TL;DR
- CISA released an updated cyber incident reporting form on November 9, 2026 within its existing Incident Reporting Portal, with more granular questions on malware, social engineering, hacking techniques and insider threats, and observed-activity questions based on MITRE ATT&CK.
- Reporting through the form is mandatory for federal civilian agencies and for certain TSA- and Coast Guard-regulated entities, and voluntary for everyone else; the broader CIRCIA mandate is still awaiting a final rule.
- A single internal intake record, structured around the fields regulators actually ask for, lets one set of facts serve CISA, state breach laws and GDPR Article 33 without contradictions.
What CISA changed, and what it did not
Some early coverage described a new reporting portal. The portal is not new. CISA moved its incident reporting form to the CISA Services Portal in August 2024, with Login.gov sign-in and the ability to save and share reports. The November 2026 change is to the form itself. According to CISA’s announcement, questions about the type of incident are now more comprehensive and ask whether the incident involved malware, social engineering, hacking techniques or an insider threat. Questions about observed activity now use the MITRE ATT&CK framework. CISA says the goal is to correlate related threat activity, so that what looks like a series of separate incidents can be recognised as one campaign.
CISA’s FAQ on the form adds that duplicate questions were removed and that the online form is now the preferred reporting channel, although email reports to Contact@cisa.dhs.gov are still accepted. The portal allows submission without signing in. Signing in through Login.gov with a work email lets the reporter save drafts, track a report and follow up with CISA. Help Net Security, describing the portal, reports that it asks for personal information only where it is needed to understand the incident. Malicious files go through a separate malware analysis form, linked by the CISA incident ID.
Who has to use it
For most private companies, reporting to CISA is still voluntary. CISA identifies two groups that must report:
- Federal civilian executive branch agencies, under binding operational directives and OMB memoranda M-25-04 and M-17-12.
- Entities already required to report to CISA, such as certain organisations regulated by the Transportation Security Administration or the U.S. Coast Guard. CISA says these must use the new form.
The larger requirement is still on hold. The Cyber Incident Reporting for Critical Infrastructure Act of 2022 (CIRCIA) will require covered critical infrastructure entities to report substantial cyber incidents within 72 hours and ransom payments within 24 hours once the rules take effect. CISA proposed its rule in April 2024 and missed the October 2025 statutory deadline for a final version. Nextgov/FCW reports that the final rule went to White House review on October 1, 2026 and was still listed as pending when the form changed. Until it is published and in force, CIRCIA deadlines do not apply.
Why one intake record beats three separate drafts
The new form asks for incident detail in a structured way. Data protection regulators, state attorneys general and sector regulators all ask for overlapping facts with different deadlines and emphasis. GDPR Article 33 requires notice to the supervisory authority within 72 hours where feasible. That notice must describe the nature of the breach, the categories and approximate numbers of people and records affected, the likely consequences and the measures taken, and it may be given in phases. New York’s breach law requires notices to the Attorney General, the Department of State and the State Police. Financial institutions face their own clocks under the amended Regulation S-P and New York’s cybersecurity regulation, where regulators increasingly expect to see the decision trail, not a polished summary.
When each notice is written from scratch, inconsistencies creep in: a record count that differs between the CISA report and the attorney general letter, or a discovery date that moves. Regulators compare filings, and plaintiffs’ lawyers do too. A single record that every notice draws from avoids that problem. It also makes multi-jurisdictional compliance manageable rather than improvised.
The fields a unified intake record needs
Build the record once, keep it in the incident ticket, and update it as facts change. A workable structure:
- Timeline anchors. When activity started, when it was detected, and when the organisation became aware that personal data was affected. GDPR, state laws and CIRCIA each start their clocks from a different event, so record all three with sources.
- Incident type and technique. Use CISA’s categories (malware, social engineering, hacking techniques, insider threat) and map observed behaviour to MITRE ATT&CK technique IDs. This is the part of the record the new form will reward.
- Entry vector and affected systems. Which account, vendor or vulnerability was used, and which systems and data stores were reached. Tie this to the data inventory so the next field is not guesswork.
- Personal data affected. Categories, approximate number of individuals and records, jurisdictions of residence, and whether sensitive data such as health or government identifiers is involved. This field drives every privacy notice.
- Risk assessment. Likely consequences for individuals and the reasoning behind any decision not to notify. Guidance such as Lithuania’s breach risk assessment guidance is a useful model for documenting that reasoning.
- Containment and remediation. What was done, when, and by whom, including credential resets and evidence preservation.
- Indicators and artefacts. Hashes, domains and malware samples, handled under legal privilege where appropriate. Samples go to CISA through the separate malware form.
- Notification log. Each authority and audience notified, the date, the version of facts used, and any follow-up owed. Keep it consistent with any phased GDPR reports.
Two discipline points make the record work. Keep personal data out of the technical narrative unless it is needed, which matches CISA’s own request on the portal. Mark every fact as confirmed or provisional, because early notices are usually corrected later and the record should show why.
Practical steps this quarter
- Walk through the updated CISA form with the security operations lead and note which questions your current incident ticket cannot answer.
- Add ATT&CK technique fields to the ticket template so analysts tag behaviour during the investigation, not afterwards.
- Build a jurisdiction matrix covering GDPR, U.S. state laws and other regimes where you have customers, such as Canada’s PIPEDA breach notification rules, each mapped to the intake fields it needs.
- Decide in advance who may file a voluntary CISA report and on what legal review. CIRCIA reports will carry statutory protections once the rule takes effect. For voluntary reports today, check what protections apply and what you are comfortable disclosing.
- Run a tabletop exercise using a realistic scenario, such as an infostealer campaign like the one disrupted in Microsoft’s action against Lumma Stealer, and produce all three notices from one record.
Frequently asked questions
Does filing with CISA satisfy GDPR or state breach laws?
No. CISA is not a data protection authority or a state attorney general. Each notification duty must be met separately. A shared intake record makes that faster and more consistent.
Is the CIRCIA 72-hour deadline in force?
Not yet. The final rule was under White House review in November 2026. The deadlines will apply only once the final rule is published and takes effect.
Should we include customer names in a CISA report?
Generally not unless it is necessary to understand the incident. CISA’s portal asks reporters to limit personal information, and the technical detail is what helps the agency spot campaigns.
Do we need to sign in to report?
No. Signing in with Login.gov is optional. It does let you save drafts, track the report and follow up with CISA.
Write it once, report it everywhere
CISA’s updated form is a federal agency asking for cleaner data so it can connect incidents across victims. Privacy teams can apply the same approach inside their own organisation. When security, privacy and legal work from one structured record, the CISA report, the attorney general letter and the Article 33 notice will give the same facts in the same terms. If a regulator later compares them, it will find them consistent.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.