Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
Sweden’s data protection authority, Integritetsskyddsmyndigheten (IMY), has written about a privacy problem that AI agents make harder to ignore: when you connect an agent to your inbox, calendar or chat apps, you also give it data about everyone you deal with. In a blog post published on November 19, 2026, two IMY specialists set out the questions people should ask before setting up a personal AI agent and offered three practical tips. The post is aimed at consumers, but almost every point applies even more strongly to an organization that gives agents access to employee mailboxes, shared drives and business systems.
TL;DR
- IMY published a blog post on November 19, 2026, on how personal AI agents can affect the privacy of people who never chose to use them.
- It advises users to check what the agent stores and how data is used, limit its access, and take care with information about others, including avoiding unrestricted access to systems, storage and backups.
- IMY also says that an agent’s autonomy does not remove the service provider’s responsibility for its basic design, including what tools and data it can reach and what it keeps.
What IMY actually published
The post, titled “Personliga AI-agenter – vems uppgifter ger vi tillgång till?” (“Personal AI agents – whose data are we giving access to?”), was written by David Suh, a lawyer, and Petter Flink, an IT and information security specialist at IMY. It appeared on the IMY blog, not as a formal guideline or decision. That matters for how much weight to give it. It is a regulator explaining its thinking, not a binding rule.
Some summaries said IMY urged people not to give AI tools information about others “without consent.” The post does not put it that way. It suggests telling your contacts that you use an AI agent, asking whether they want any conversations excluded or deleted before the agent is switched on, and checking deletion options if their data has already been shared. That is advice about consideration and transparency, not a statement that consent is the required legal basis.
The core problem: other people’s data
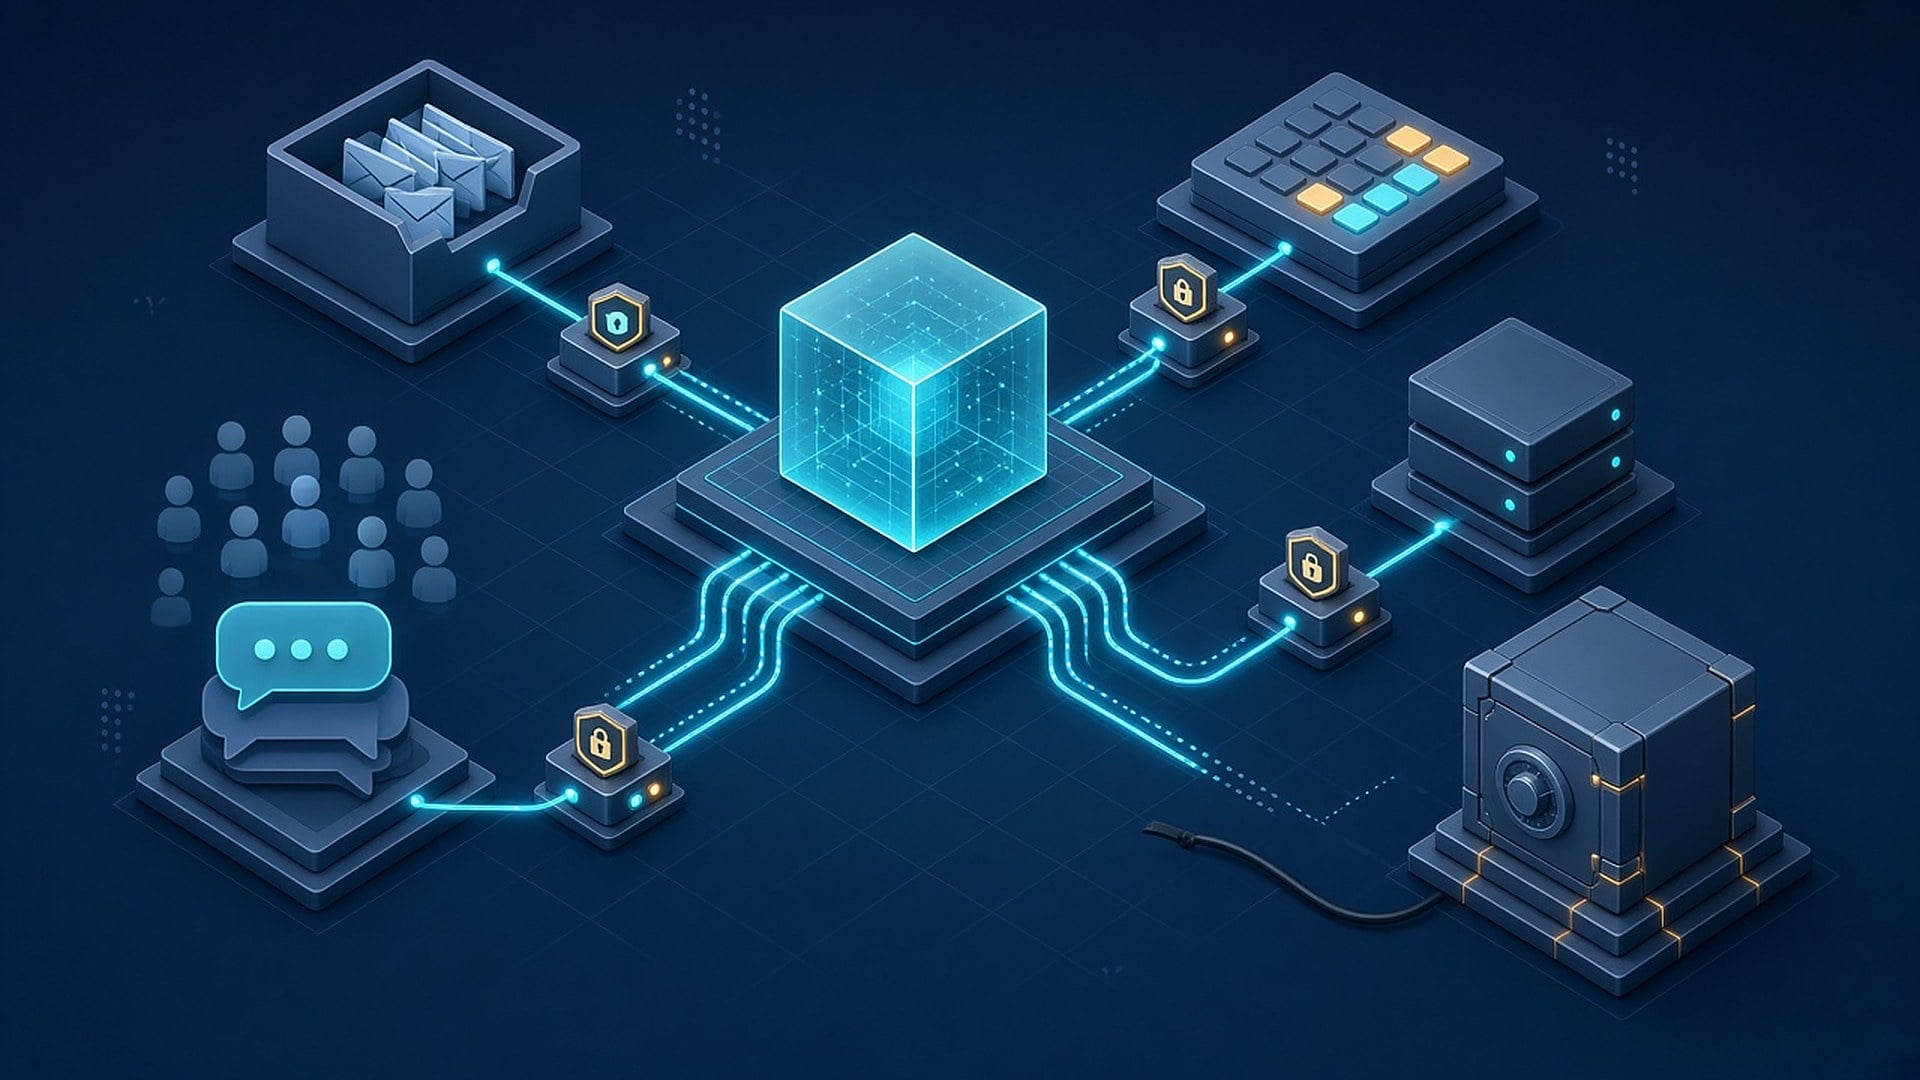
IMY’s starting point is simple. A social media or messaging account contains much more than the account holder’s data. It includes messages from friends, details about colleagues and family, and photos of acquaintances. Connecting an agent to that account means the agent can affect people who never used the service and may have actively chosen to avoid it.
The post highlights two risks:
- Encryption can be undermined at the endpoint. End-to-end encryption protects a message in transit, but IMY notes that this protection loses its purpose if the recipient runs an agent that can expose the content. Depending on the service, the data may also go to the provider and be used for other purposes, such as AI training.
- Combining data produces new conclusions. Data that seems harmless on its own can be linked into conclusions that are later used elsewhere.
IMY gives an example. An agent with access to your email, your colleagues’ shared calendars and the open web sees a colleague’s blocked afternoons with no details, a detailed public career profile and a request for a summary of their project results. It might conclude that the colleague is looking for a new job. That might not matter much to you, IMY says, but it could matter a great deal if your manager uses a similar agent. The conclusion can affect someone whether it is true or not.
The post also warns that agents built as ongoing assistants or companions may build profiles of friends, relatives and colleagues over time. The people profiled may not know it is happening, which makes it hard for them to see what was collected, what conclusions were drawn, or how to limit the processing.
IMY’s three tips
The post closes with three steps for users. Translated and condensed:
- Find out what the agent stores and how data is used. Review the settings for access, retention and uses such as AI training. If you cannot set the limits you want, consider another service or do not connect certain accounts, such as social media or direct messaging.
- Limit the agent’s access. Think about which accounts and sources the task really needs. Does it need your entire inbox and every account, or can you choose a subset? IMY writes that users should avoid giving the agent unrestricted access to their systems, storage and backups, and should review permissions regularly as their needs change and services are updated.
- Be careful with information about others. Pay special attention to data the other person might see as sensitive, tell your contacts you use an agent, and offer to exclude or delete conversations.
The part aimed at providers
The most important sentence for businesses is easy to miss. IMY writes that an agent’s degree of autonomy does not remove the service provider’s responsibility for its basic functionality. What the agent can do, and the risks it creates, depend on which tools it can use, which data it can reach, what it stores and what limits are built in. The fact that not every action can be predicted, IMY says, does not mean those conditions do not matter or can be left uncontrolled. Services should make it easy to understand what the agent can access and how it reasons, let users limit what it reads, stores and uses, and set restrictive defaults.
That is close to the GDPR’s principle of data protection by design and by default in Article 25. It also fits Recital 18, which says that even when individuals use a tool for purely personal or household activities, the GDPR still applies to the controllers or processors that provide the means for that processing.
What this means for organizations deploying agents
A person using an agent for private life may fall under the GDPR’s household exemption. An employer that deploys agents across its workforce does not. The organization is the controller, and the colleagues, customers and correspondents in those mailboxes are data subjects. Here is how IMY’s consumer advice translates into enterprise controls:
- Least privilege, by design. IMY’s own guidance on access control applies a need-to-know principle: carry out a needs and risk analysis before assigning permissions, document it, and restrict privileged access. Treat each agent as a user with its own scoped identity, not as an extension of a person’s full account.
- Keep backups and archives out of scope. IMY specifically names storage and backups. Backups often hold the oldest and least curated data, and an agent rarely needs them for routine tasks.
- Map what the agent touches. Add agents to your records of processing and data flows. Our GDPR data mapping guide covers how to document new systems that pull from several sources.
- Run a DPIA before broad rollout. An agent that combines email, calendars and web data to draw conclusions about people is the kind of new, large-scale processing that calls for a data protection impact assessment under Article 35.
- Control memory and inference. Set retention limits for what agents remember between tasks, and decide whether they may draw conclusions about individuals at all. IMY’s job-search example is a ready-made test case for HR and management uses.
- Check the vendor’s training terms. Confirm whether prompts, connected data and outputs can be used to train models, and contract accordingly.
- Review permissions on a schedule. IMY’s advice to revisit permissions as needs and services change fits quarterly access reviews, especially after vendor updates that add new tools or connectors.
These questions are already becoming live. Our coverage of an AI assistant that keeps the inbox shows the same tension in a commercial product, and the industry talk of organizations running thousands of AI agents shows how quickly scale can outrun permission reviews. For a wider view of the legal exposure, see our roundup of AI privacy issues. Encryption questions also come up when providers build AI into messaging, as in our piece on Meta’s encrypted AI chatbot.
A pattern from IMY
This is not IMY’s first look at consumer technology that captures bystanders. It has previously issued guidance on smart glasses, another case where one person’s choice of device affects people nearby. The common thread is that privacy protection cannot depend only on the choices of the person using the product.
Frequently asked questions
Is IMY’s AI agent post binding guidance?
No. It is a blog post by IMY staff. It shows how the regulator thinks about the issue, but it is not a formal guideline or decision.
Does a private user need consent from contacts before using an agent?
The post does not say that. It recommends telling contacts and offering to exclude or delete conversations. Purely personal use may fall under the household exemption, although the provider of the agent remains subject to the GDPR.
Does the household exemption cover employees using agents at work?
No. Work use is processing on behalf of the employer, which is the controller and must meet GDPR obligations for the data the agent handles.
What is the single most useful control for agents?
Scoped access. Give each agent only the accounts, folders and functions a task needs, preferably read-only, and review those permissions regularly.
Last word
IMY’s post ends with a line worth keeping in mind: even if an AI agent works for one person, privacy protection covers everyone. For organizations, that means designing agents for the people in the data, not just the people giving the instructions.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.