Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
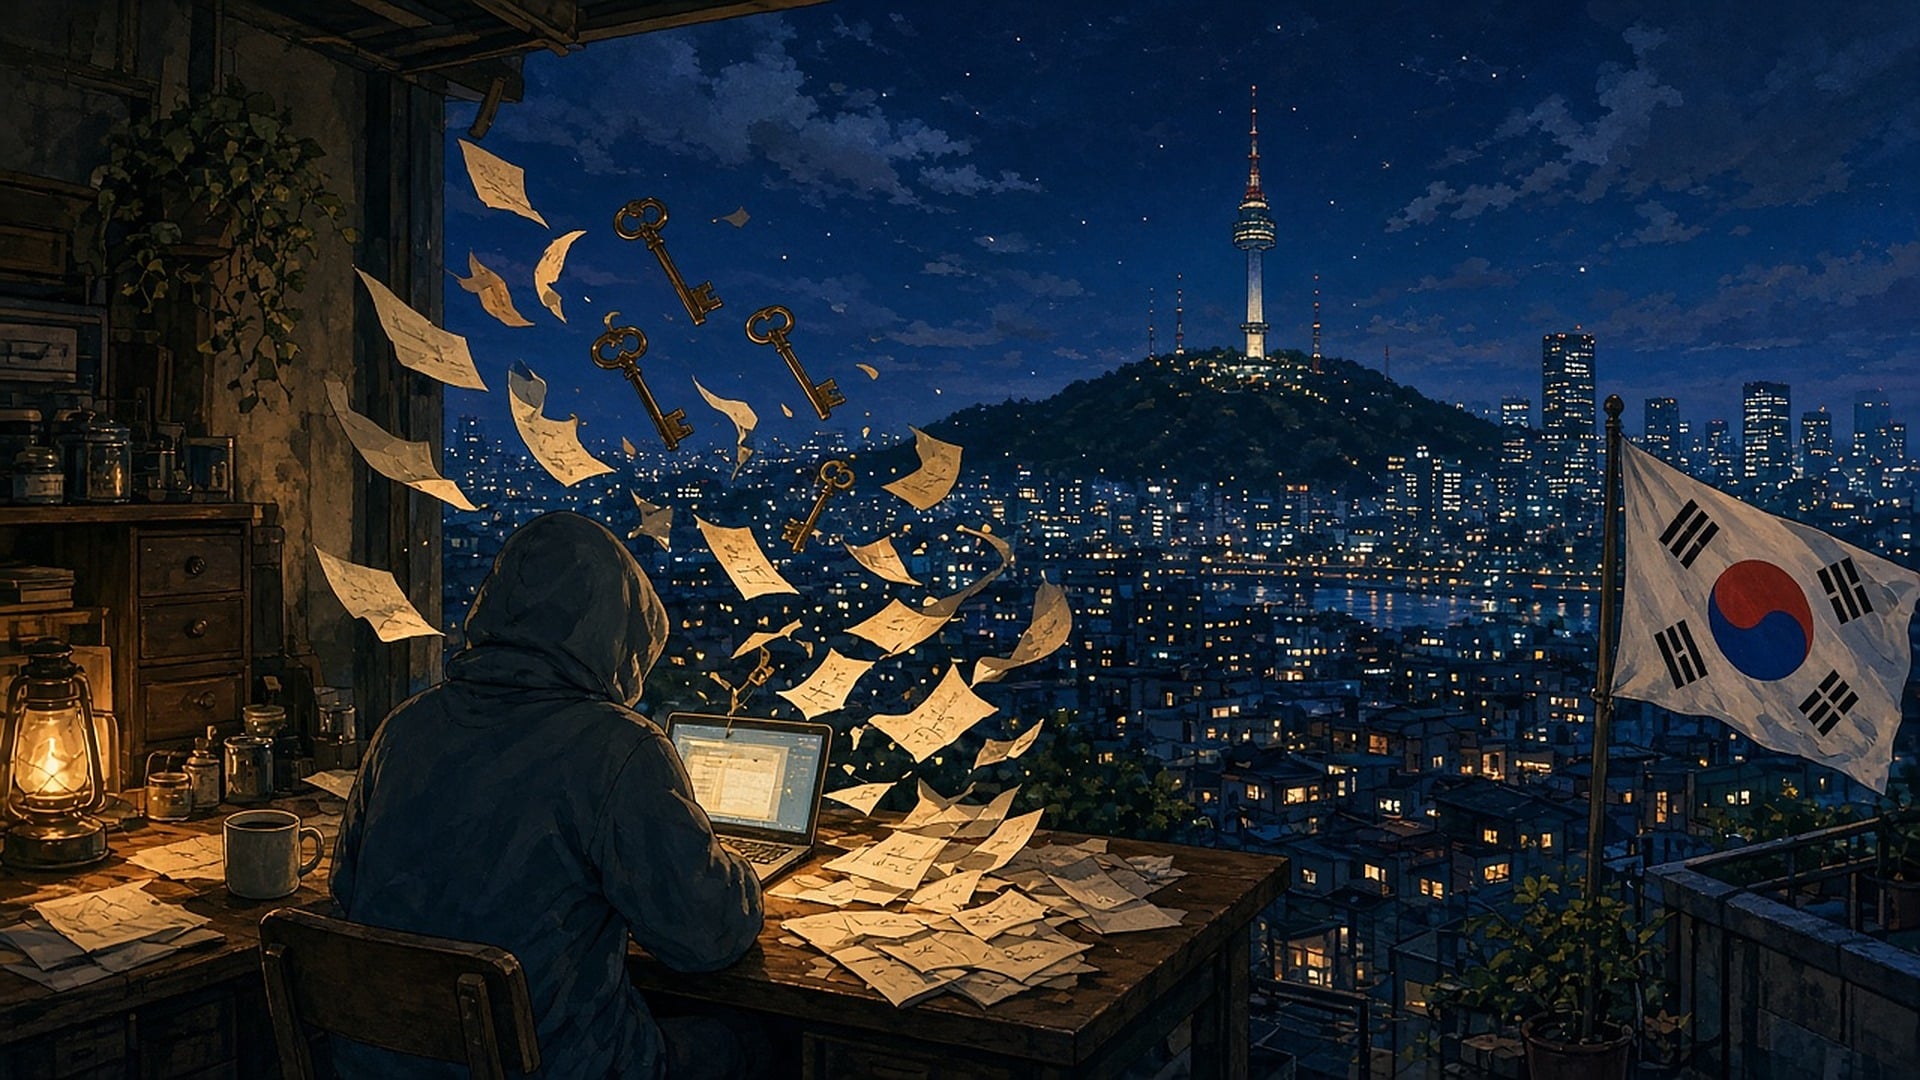
The most unsettling detail in the investigation into this autumn’s attacks on South Korean financial firms is not the size of the breach. It is the résumé. According to CrowdStrike, the person it believes was behind the campaign asked an AI coding assistant to write a security researcher CV that listed the results of the hacking as accomplishments, and in doing so supplied an age, a university, a Telegram handle and a home city. That is not the behavior of a disciplined state operator. It looks like someone with modest skills and outsized tools, which is exactly what security experts are now warning about.
“Basically any pedestrian, non-hacker can take these frameworks and start leveraging them to go after different targets,” CrowdStrike’s senior vice president of counter adversary operations, Adam Meyers, told The Washington Post for a November 1 report on what the paper called a cybersecurity reckoning. For privacy and compliance teams, the question is what changes when the pool of capable attackers suddenly gets much larger, and what does not.
What happened in South Korea
Beginning in late September 2026, a series of South Korean financial companies disclosed intrusions. On October 14, the Financial Services Commission said the number of affected firms had reached 16, more than double the seven first reported, and that about 100,000 records containing personal information had been exposed, according to The Korea Times. The affected firms included four banks, Shinhan, KB Kookmin, BNK Busan and Hana, along with savings banks, credit finance companies, electronic payment providers and cryptocurrency businesses. The leaked data included names, contact details and resident registration numbers. Regulators said they had found no evidence that account or card numbers were compromised. Media counts of banks that were targeted, as opposed to confirmed as breached, have run higher.
Earlier, Shinhan Bank said personal information of about 25,000 customers had been compromised, and KB Kookmin said 119 customers were affected, Reuters reported. South Korean police opened an investigation.
CrowdStrike published its analysis on October 7. Its researchers found attacker-controlled open directories that held AI coding-assistant session histories, configuration files for a tool called ARTEX and the assistant’s memory files. ARTEX is a recently released open-source agentic penetration testing tool developed in China. CrowdStrike said the ARTEX instance used DeepSeek as its main language model, with other models used in additional sessions. At one bank, the attacker reportedly breached a loan progress inquiry service used by financial brokers. At another, the target was an employee mobile work-support system. In one session, according to Reuters, the attacker asked the assistant where threat actors usually sell Korean breach data.
Two points of precision matter. CrowdStrike assessed “with moderate confidence” that the actor was a Chinese speaker and financially motivated, and said the personal details in the résumé likely belonged to the attacker but could not definitively identify the person. Reports describing a “26-year-old in China” are therefore describing CrowdStrike’s lead, not a confirmed identification or a charge. And the toolset was not a single chatbot. It was an agentic attack framework driven by several large language models, used alongside conventional offensive techniques.
What the experts actually said
Meyers’s message has two halves, and both are useful.
The first is about scale. On a press call, he said the campaign was significant “because it allows one human to target many customers in a very short period of time using the power of AI,” Reuters reported. He told the Korean newspaper Hankyung that CrowdStrike was tracking six or seven “agentic attackers” and that what had surfaced so far was likely the tip of the iceberg.
The second half is reassuring, and often left out. In the same interview he said the attacker’s technical ability was not high, that CrowdStrike had seen no fundamentally new attack techniques in the AI-driven attacks it had observed, and that properly designed and deployed endpoint detection and response should be able to detect and block such attacks. In other words, AI made familiar methods faster and cheaper. It did not make them invisible.
Korean regulators reached a similar conclusion from the other direction. In its October 14 review, the Financial Services Commission said that 130 of 555 financial firms inspected, or 23.4 percent, had security deficiencies, including missing patches, unsupported systems, no 24-hour monitoring and weak authentication for external systems. The attackers did not need to be brilliant if the doors were already open.
Why this is a privacy problem, not just a security one
When the attacker population grows, the probability that any given organization’s exposed weaknesses are found rises with it. That has three consequences for privacy programs.
- Breach likelihood assumptions change. Risk assessments, DPIAs and vendor reviews often assume that sophisticated attacks require sophisticated attackers. That assumption is weaker now. A low-skill actor with an agentic framework can probe many targets at once.
- Data minimization becomes a security control. The Korean breaches exposed resident registration numbers. Data an organization does not hold cannot be stolen, and records it deletes on schedule do not show up in someone else’s Telegram sales channel.
- Accountability moves up. The Korean regulator has said it will pursue measures to hold CEOs and boards more accountable, a direction we covered when South Korea made the CEO personally responsible for data breaches. Similar expectations are spreading elsewhere, and recent record penalties such as the Coupang breach fine show regulators are prepared to act on them.
We looked at the regulatory response to an earlier AI-orchestrated campaign in our analysis of agentic AI cyberattacks. The Korean case adds something new: evidence that the operator does not need to be a capable professional.
Seven controls that matter more when attackers multiply
None of these are new. What is new is the cost of skipping them.
- Patch internet-facing systems on a deadline. Agentic tools are good at finding known, unpatched vulnerabilities across many targets quickly. Treat exposure windows in days, not quarters.
- Retire or isolate unsupported systems. The Korean inspection found unsupported systems among the most common gaps. If a system cannot be patched, it should not be reachable from the internet.
- Harden broker, partner and employee portals. Two of the reported entry points were a service used by external brokers and an employee mobile system. Secondary portals often get less scrutiny than the main customer site.
- Monitor around the clock or pay someone to. Speed is the attacker’s advantage. Detection that only runs in business hours gives an automated campaign a free night.
- Minimize high-value identifiers. Inventory where national ID numbers, government identifiers and similar data are stored, and reduce, tokenize or delete them where you can.
- Extend the review to vendors. Many organizations’ most exposed systems are run by third parties. Our guide to third-party cyber risk covers what to ask.
- Rehearse breach notification. More incidents mean more notification decisions under tight legal deadlines. Know in advance who decides, what the regulator expects and how affected people will be told.
Where Captain Compliance fits
Captain Compliance is a privacy platform, not an endpoint security product, and it will not stop an intrusion. Where it helps is in the privacy side of the same problem: data mapping that shows where sensitive identifiers live, assessment workflows that record why a risk was accepted or mitigated, data subject request handling that depends on knowing what you hold, and website scanning that shows which third-party scripts can reach visitor data. Those records shorten breach response and make the accountability conversation with a regulator or board more concrete. They do not replace a security program, and no tool can guarantee that a breach will not occur.
Frequently asked questions
Has anyone been charged over the South Korean attacks?
As of November 2, 2026 we have seen no public report of charges. South Korean police opened an investigation in October. CrowdStrike’s identification of a likely suspect is an assessment based on digital traces, which the company itself said was not definitive.
Did the attacker use a public chatbot like ChatGPT?
CrowdStrike’s report describes an open-source agentic penetration testing framework, ARTEX, driven by several large language models, and sessions in an AI coding assistant. That is more structured than simply chatting with a public chatbot, though it was still assembled from publicly available tools.
Are AI-assisted attacks harder to detect?
Not according to CrowdStrike’s Meyers, who said the techniques observed were not fundamentally new and that properly configured endpoint detection should catch them. The difference is speed and volume, which shrinks the time defenders have.
Should we ban AI coding assistants internally because attackers use them?
Banning internal use does not affect what attackers do. The more useful step is to govern how your own teams use these tools, including what data they may paste into them, and to make sure the assistants’ session logs and memory are secured, since in this case those artifacts exposed the attacker.
Does this change our breach risk assessment?
It should change the likelihood side. If a control was justified on the basis that exploiting a weakness required rare skill, revisit that reasoning. Our earlier write-up on the first AI-orchestrated espionage campaign shows how quickly that assumption has eroded.
The résumé problem
The attacker in South Korea was caught out, at least provisionally, because the AI tools kept a record of everything, including a careless request to turn a crime into a CV. That is a reminder that AI-assisted work leaves traces, for attackers and defenders alike. The open question for companies is whether their own records, of what data they hold, which systems are exposed and which risks they chose to accept, are as complete as the attacker’s turned out to be. In the next breach review, that is likely to be the first thing a regulator asks to see.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.