Maria Sanzio
Maria “Belen” Sanzio is a Data Privacy Engineer & Specialist. She is a Buenos Aires-based Privacy Engineer dedicated to bridging the gap between legal requirements and technical execution. Currently focused on operationalizing privacy and onboarding here at Captain Compliance, she specializes in transforming complex global regulations like the GDPR and Argentina’s LPDP into scalable, automated workflows while handling integrations of DSARs, consent platforms, and privacy notices.
Posted articles 153 TOTAL
States Are Begging Congress to Renew Cybersecurity Grants — And the Clock Is Ticking
State cybersecurity officials from Florida, New York, and Tennessee took their case directly to Congress this week, warning lawmakers that without renewal…
What is the _lc2_fpi Cookie? A Guide to Compliance and Tracking
If you have ever run a privacy audit or pulled a cookie scan on your company’s website, you have likely run into…
Ideal Image Data Privacy Lawsuit: A $3.5 Million Settlement That Should Make Every Website Owner Reconsider Their Tracking Strategy
Aspen Dental settled for $18.7 million and Ideal Image settled a privacy lawsuit for $3.5 million.
 COOKIES
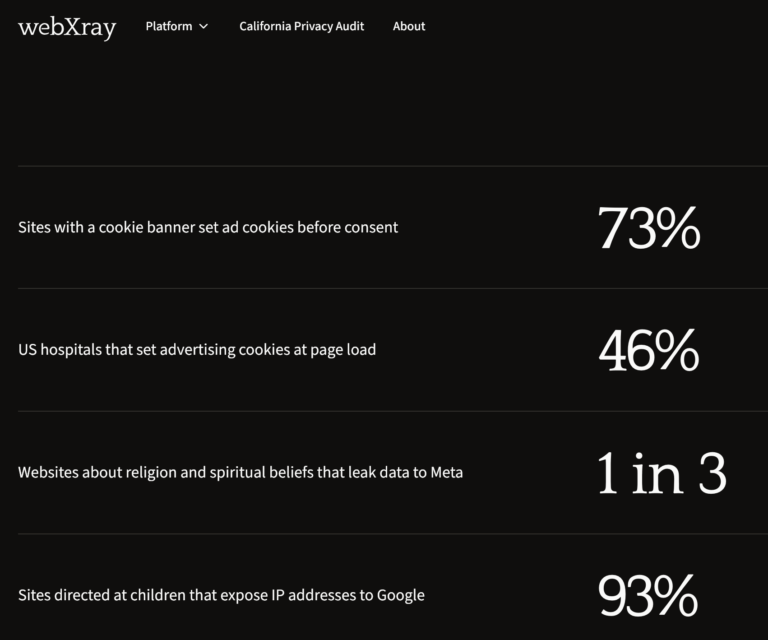
webXray: The Privacy Forensics Company That’s Rewriting the Rules of Digital Accountability
The digital privacy industry has, for years, operated on a kind of polite fiction: put up a cookie banner, tick a few…
 COOKIES
Cookie Governance
Everything organizations need to build, maintain, and scale a compliant cookie governance program — from policy and framework to country-by-country requirements, Global…
Nolan Klein: The Go-To Defense Attorney When ADA Lawsuits Come Knocking
While ADA Lawsuits are not nearly as expensive as data privacy litigation they still should be taken seriously and we have found…
 DATA
Oklahoma AG Sues Temu: Unlawful Data Harvesting, Spyware Allegations, and IP Theft in Latest Blow to Chinese E-Commerce Giant
Comprehensive analysis of Oklahoma Attorney General Gentner Drummond’s lawsuit against Temu and its place in the growing wave of state actions against…
The Microphone You Forgot to Mention
There’s a moment happening in exam rooms across the country that nobody’s talking about — at least not to the patient.
 COOKIES
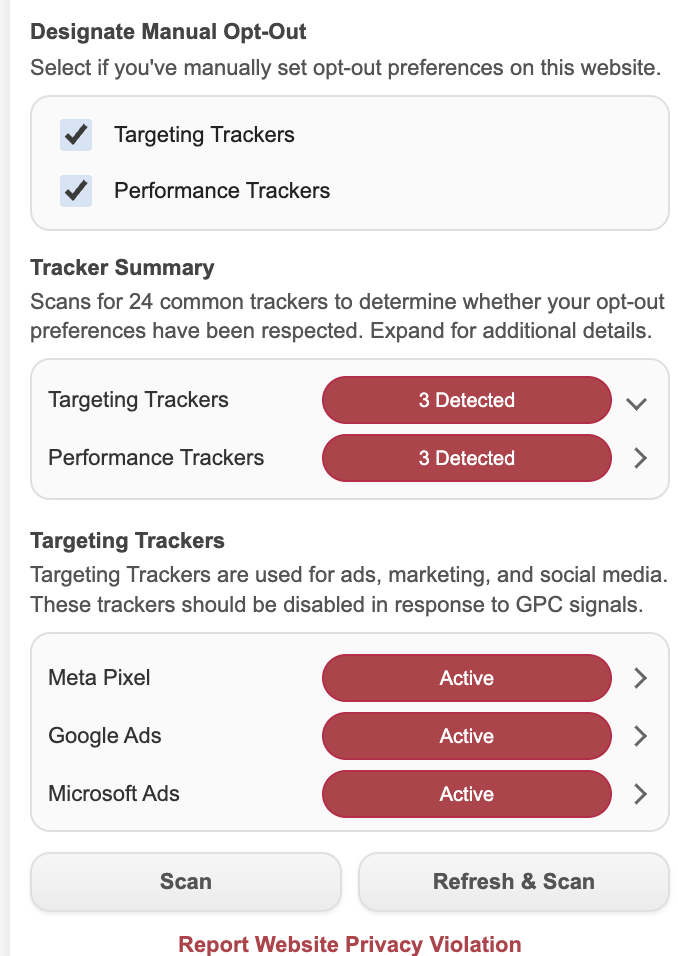
“Accept All” Isn’t Consent. Latvia’s Privacy Regulator Finds Cookie Banners Not Working
Latvia’s Data State Inspectorate just published a blunt assessment of how badly most websites are handling cookie consent — and the problems…
Millions of Americans Used State Health Insurance Exchanges. Many May Not Have Realized Their Data Was Flowing to Big Tech.
The next major privacy battle in the United States may not involve social media, smart devices, or AI chatbots.
 GOVERNANCE RISK AND COMPLIANCE
Choosing the Right GRC Tool: What the Vendor Demo Won’t Tell You
Most organizations pick a GRC platform the wrong way. Here’s how to do it right. There’s a familiar pattern in how compliance…
 AI
Governments Want Access Before AI Launches. The U.S. and U.K. Just Moved the Industry Closer to Mandatory Pre-Deployment Oversight.
The era of governments regulating artificial intelligence after deployment may already be ending.
Check your own site
See what your website is actually sending.
Run a free privacy audit and find the cookies, pixels, session-replay tools, and trackers running right now — plus the ones that commonly show up in privacy claims. A real review of your site, not just a scan.