Graeme Whiles
Graeme Whiles is an editor at Captain Compliance and a seasoned copywriter and marketing expert with a considerable amount of experience in compliance, particularly concerning GDPR regulations within content marketing and eCommerce sectors.
Posted articles 105 TOTAL
How the Legal Basis for AI Training Is Framed in Data Protection Guidelines: A Multi-Jurisdictional Doctrinal Analysis
I. The rapid expansion of artificial intelligence (AI) systems trained on vast quantities of personal data has placed unprecedented strain on the…
 COMPLIANCE
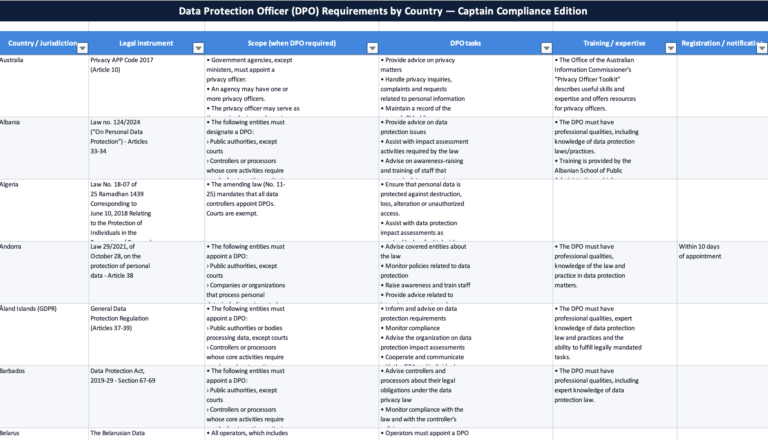
Data Protection Officer (DPO) Requirements by Country
The role of a Data Protection Officer (DPO) has evolved from a best-practice recommendation to a mandatory legal requirement across dozens of jurisdictions.
 GDPR
The ICO Reframes International Data Transfers
What the Updated UK GDPR Guidance Means for Organisations The UK Information Commissioner’s Office (ICO) has signaled a meaningful evolution in how…
 AI
Senate Unanimously Passes DEFIANCE Act
Victims Gain Right to Sue Over Nonconsensual Deepfakes Amid Grok AI Controversy on X In a swift and unanimous vote, the United…
AI Privacy Harm at Platform Scale: What X’s Grok Restrictions Signal for AI Compliance
X’s recent changes to Grok’s image-editing functionality reflect a belated but material shift toward a more defensible compliance posture in jurisdictions that…
PSD2 Compliance
The European Union’s revised Payment Services Directive, commonly known as PSD2, has fundamentally transformed how financial institutions, payment service providers, and third-party…
 AI
The Dawn of Agentic AI: Privacy Implications and the ICO’s Forward-Looking Vision
The UK’s Information Commissioner’s Office (ICO) has always been proactive about emerging technologies that touch on personal data.
 GDPR
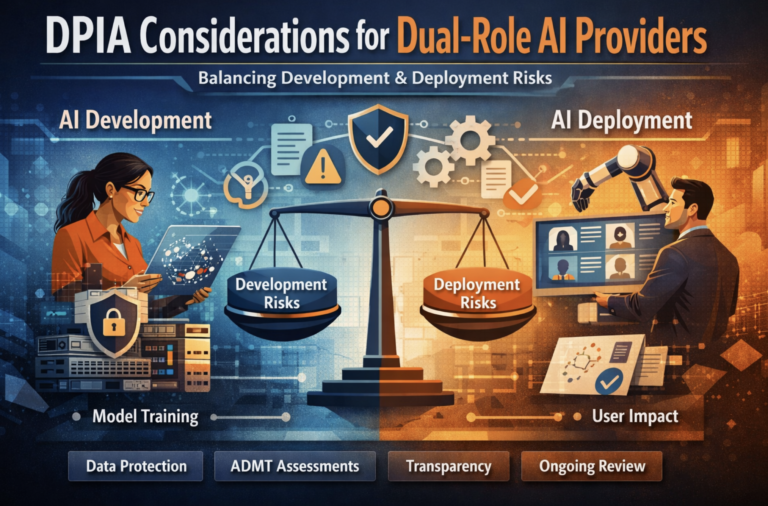
DPIA Considerations for Dual-Role AI Providers: When Building and Deploying AI Creates Overlapping Privacy Risk
As artificial intelligence becomes embedded into enterprise products, platforms, and services, a growing number of organizations find themselves occupying a dual role:…
 AI
The EU’s New AI Code of Practice: A Practical Guide to Labeling Deepfakes and Why It Matters
The European Union has long positioned itself as a global leader in tech regulation, and its latest move on artificial intelligence is…
The Grok Deepfake Crisis: A Biometric Privacy Disaster That Regulators Missed
When Ofcom launched its investigation into X under the UK’s Online Safety Act over Grok’s image generation capabilities, the headlines focused on…
GDPR EU Poised to Share Citizens’ Biometric Data with U.S
European Union governments are moving toward agreements that would allow U.S.
Data Protection Technologies
As a business owner you can no longer afford to treat data protection as an afterthought.
Check your own site
See what your website is actually sending.
Run a free privacy audit and find the cookies, pixels, session-replay tools, and trackers running right now — plus the ones that commonly show up in privacy claims. A real review of your site, not just a scan.