Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.
On 16 November 2026, visitors to websites run by Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, HSBC and Equifax were served malicious JavaScript that none of those companies wrote. The code did not arrive through a break-in at each organisation. It rode inside the snippet that each site loads from Optimizely, a widely used web experimentation platform, after an attacker abused a flaw in Optimizely’s service and wrote code into customer projects. The episode is the clearest recent example of a risk most privacy and security programmes still treat as an afterthought: every third-party script on a page runs with the same access to the visitor’s browser as the site’s own code, and it can change without the site owner touching anything.
TL;DR
- Security researcher Scott Helme of Report URI found malicious code in 188 Optimizely snippets belonging to 178 organisations on 16 November 2026, and says the real number is likely higher.
- The injected script swapped cryptocurrency wallet addresses, skimmed card details typed into site forms, collected cookies and screenshots, and tried to load iOS exploit kits on older iPhones and iPads.
- Optimizely says an unauthorised party exploited a vulnerability in its Experimentation product, and that it has fixed the flaw, removed the code and secured affected accounts.
What happened, and what the early headlines got wrong
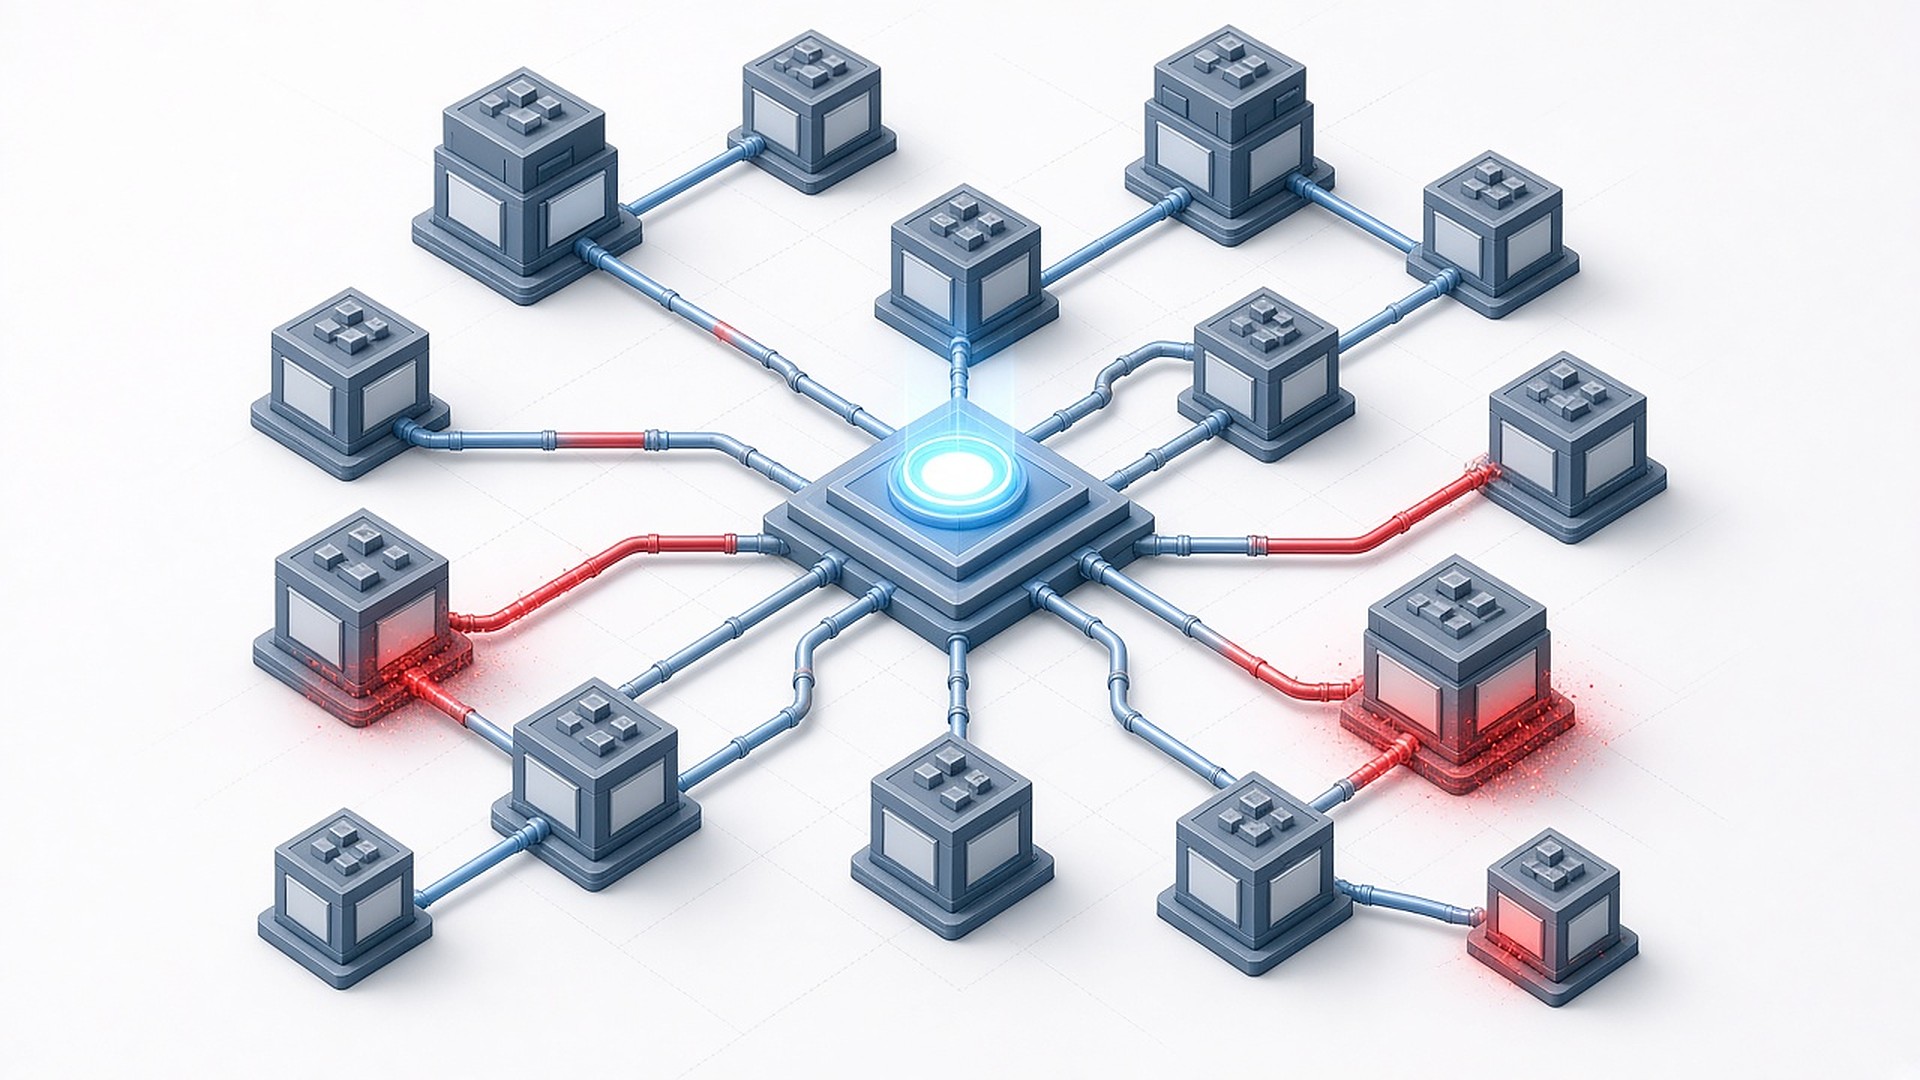
Optimizely Web works by having each customer place a small JavaScript snippet on its pages. The snippet is fetched from Optimizely’s content delivery network and contains Optimizely’s own code, the customer’s experiments, and an optional block of custom “Project JavaScript” that runs on every page. According to the technical write-up published by Report URI, the attacker inserted a loader into that Project JavaScript field. The rest of each file was untouched, and it was still served from Optimizely’s trusted host with Optimizely’s certificate. The loader pulled a second script, track.js, from an attacker-controlled domain.
Report URI’s timeline puts the first injection at 04:21 UTC on 16 November, with cleanup sweeping through most affected snippets between roughly 20:40 and 21:10 UTC. By 23:11 UTC, the researchers say, every infected file they were tracking was clean. The payload was rebuilt 26 times during the day, and a card skimmer was added to it at 13:43 UTC, so what a visitor was exposed to depended on when they arrived.
Optimizely acknowledged the incident on its service status page, stating that an unauthorised party exploited a vulnerability in Experimentation and used it to add malicious JavaScript to some customer projects, that the vulnerability has been fixed and the injected code removed, and that it has secured affected user accounts and added protections against unauthorised code delivery. In a statement to BleepingComputer, the company located the flaw in the Experimentation account signup flow and said it had ended active sessions, revoked tokens and notified affected customers. Salesforce told the same outlet it had disabled Optimizely scripts as a precaution while it investigated.
Some early summaries described this as a breach of 178 websites aimed at “iPhone data.” That framing is imprecise in two ways. First, researchers found the code in Optimizely-hosted files tied to 178 organisations; Report URI stresses that a site can be hit this way without its own code or infrastructure ever being breached, and Reuters said it could not confirm whether the code was successfully used in each case. Second, the iOS component was not a data grab from phones in the usual sense. It loaded the Coruna and DarkSword exploit kits in a hidden frame on devices running older iOS versions, which is an attempt to compromise the device itself. The confirmed financial loss at the time of writing was modest: Report URI counted roughly $7,000 in cryptocurrency received by the attacker’s wallets, and says it has no visibility into how many cards, cookies or screenshots were captured.
What the payload actually did
Each capability maps onto a different legal and operational problem for the site owner:
- Wallet address swapping. The script searched page text, form fields, the clipboard and outgoing requests for valid cryptocurrency addresses and replaced them with the attacker’s. Any site that displays payment or deposit addresses was a target.
- Card skimming. It watched form submissions and POST requests for a card number, expiry date and security code, and sent the set to the attacker once it had all three. Report URI notes that cards entered inside hosted payment iframes from processors such as Stripe or Adyen were out of reach. Cards typed into a site’s own form fields were not.
- Cookie and screenshot collection. On pages with wallet or payment wording, it sent the page URL, any cookies not marked HttpOnly, and a rendered screenshot of the page.
- Device exploitation. On iPhones and iPads, it loaded exploit chains matched to the iOS version. Readers who followed earlier reporting on a leaked iPhone exploit kit will recognise how quickly such tools move from targeted use into mass campaigns.
Report URI also tied the same actor to an earlier wave, from 13 to 16 November, delivered through scripts from other vendors such as Kissmetrics and StorifyMe. The lesson is not about one vendor.
Why this is a privacy compliance problem, not just a security one
Privacy teams already review third-party scripts, but usually through the lens of consent: which tags fire before a visitor agrees. The same inventory is also an attack surface. A tag that is perfectly lawful from a consent standpoint can still be the vehicle for an attack if its supplier is compromised.
The legal exposure follows the data, not the vendor. If card numbers with security codes were captured from your checkout form, the incident may meet the definition of a reportable breach under state laws such as California’s, where the breach notification statute in Civil Code 1798.82 treats a card number combined with a required security code as personal information. California now requires notice to affected residents within 30 calendar days of discovery, subject to law enforcement and scoping delays, and a sample notice to the Attorney General when more than 500 residents are notified. Understanding the difference between PII and PCI data matters here, because card data also brings card-network and acquirer obligations that run in parallel with statutory notice.
For organisations subject to the GDPR, the analysis turns on roles. The website operator is normally the controller for the personal data its visitors enter, and a vendor like Optimizely acts as a processor. Under Article 33, a controller must notify its supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware of a personal data breach, unless the breach is unlikely to result in a risk to individuals. A processor must tell the controller without undue delay. Whether a site’s visitors were affected is a factual question for each controller, but the clock starts on awareness, not when the vendor finishes investigating.
A seven-step script supply chain review
The steps below are meant for privacy, security and marketing teams working together.
- Build a living inventory of every script. List every first- and third-party script on each domain, who owns it internally, what it is for, which pages load it, and whether it can inject further scripts. Include scripts served from your own subdomains: Report URI found that customers who proxied the Optimizely snippet through their own domains were affected too.
- Treat vendor dashboards as production code. Fields like Optimizely’s Project JavaScript, custom HTML tags in a tag manager, or “custom code” boxes in marketing tools let anyone with access, or anyone who compromises that access, push code to your visitors. Limit who can edit them, require multi-factor authentication, and review changes.
- Deploy a restrictive Content Security Policy. Report URI crawled 256 affected organisations’ hosts: 68 had no CSP at all, 50 had a policy that allowed both the payload and the data theft, and only 24 blocked the payload. Allowlisting the vendor’s CDN does not help when the malicious code comes from that CDN. What helped was a tight script-src list and connect-src rules that block unknown destinations. Watch for ‘strict-dynamic’ and ‘unsafe-eval’, which let injected scripts through.
- Use integrity checks where the file is static, and monitoring where it is not. Subresource Integrity hashes work for versioned libraries but break on snippets that change with every experiment. For those, monitor the script’s fingerprint and alert on unexpected changes or new outbound connections.
- Keep payment fields out of reach. Hosted payment iframes kept cards out of this skimmer’s grasp. If you take cards on your own pages, PCI DSS v4.x Requirements 6.4.3 and 11.6.1 already require you to authorise payment-page scripts, confirm their integrity and detect tampering; the PCI Security Standards Council’s e-skimming guidance explains how.
- Load less, and load it later. Experimentation and analytics scripts rarely need to run on checkout, account or login pages. The same discipline used to block scripts and tracking pixels before consent can keep non-essential code off your most sensitive pages entirely.
- Rehearse the vendor-incident playbook. Decide in advance who can disable a third-party script in minutes, how you will pull logs to establish exposure windows, and who makes the notification call under each applicable law.
Contract terms that matter after a vendor incident
A strong data processing agreement will not stop an attack, but it determines how fast you learn about one and what help you get. Check that your script vendors are bound to notify you of security incidents within a defined, short window, to share technical indicators and affected project identifiers, and to cooperate with your breach assessment. Ask how they protect customer-editable code fields, whether they offer change logs and alerts for edits, and how they segregate one customer’s projects from another’s.
Your vendor’s vendors are part of the chain too. A script platform relies on CDNs, identity providers and its own subprocessors, so due-diligence questionnaires should cover them.
Frequently asked questions
We use Optimizely. Were we affected?
Optimizely says it has notified all affected customers. Report URI has published its list of affected organisations and domains. Even if you are not on either list, review your snippet’s change history and your own logs for requests to unfamiliar domains on 16 November.
Does a script injected by a vendor count as our breach?
It can. Notification duties under laws such as the GDPR and state breach statutes attach to the organisation that controls or owns the personal data. If your visitors’ data was acquired by an unauthorised person through code running on your pages, you need to assess the incident as yours, even though the vendor’s systems were the entry point.
Would a cookie consent banner have prevented this?
Only partly. Consent gating keeps non-essential scripts from loading for visitors who decline, which shrinks exposure. It does nothing for visitors who accept, and it cannot detect a trusted script that has been tampered with. Subresource Integrity has a similar limit: it suits static, versioned files, not snippets that change with every experiment.
The script you trust is the one to watch
The Optimizely incident lasted less than a day, and the confirmed theft was small. Its real value is as a stress test that most of the affected sites failed: no policy to block an unknown destination, no alert when a trusted file changed, and no quick way to know what visitors were exposed to. Every organisation that loads third-party code can run that test on itself now, before an attacker does it for them.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.