Know what’s on your site before a plaintiff’s firm does
A free privacy audit shows which cookies, pixels and trackers are running — and which ones commonly appear in privacy claims.

The existence of over 100 data protection laws underscores the importance of protecting personal data. Although there are lots of similarities between the Brazil LGPD vs GDPR, there are nuances that set them apart. Just this year new privacy laws came out and the list seems to be never ending.
If you run a global or local business with a global reach, figuring out what laws apply can be confusing. We’re here to help you with that!
Today, we highlight the differences between Brazil LGPD and EU GDPR to simplify your compliance efforts.
Key Takeaways
The Brazil LGPD bears a resemblance to the GDPR.
Slight differences exist in processing principles, data subject rights, and justification. There are also differences in the contents of privacy notices, data security rules, data breach notices, and penalties.
Compliance with one does not automatically translate to compliance with the other. An expert who understands the nuances involved can help identify the gaps.
What is Brazil’s LGPD?
Brazil approved the Lei Geral de Proteção de Dados Pessoais (LGPD) in August 2018 (the same year the GDPR took effect). LGPD unified over 20 provisions in the country’s laws protecting personal data. LGPD’s similarity with the GDPR earned it the nickname “the Brazilian GDPR.”
LGPD regulates how controllers and processors collect, process, store, and transfer personal data when the processing is carried out in Brazil, when the processing aims to offer or provide goods or services or to process data of individuals located in Brazil, or when the personal data were collected in Brazil (Article 3). Residency and Brazilian citizenship are not the test.
It doesn’t matter if the business is not operating in Brazil; the LGPD, which came into force in 2020, will apply so far as the personal data belong to a Brazilian resident or the processing happens in Brazil.
What is the GDPR?
The GDPR is the EU’s data protection law governing how personal data is collected, processed, stored, and transferred. The GDPR applies to processing in the context of an establishment in the Union (Article 3(1)) and, if the controller or processor is not established in the Union, to processing of personal data of people who are in the Union where the processing relates to offering them goods or services or monitoring their behavior in the Union (Article 3(2)). Residency and citizenship are not the test.
It is enough that the processing happens in the EU, so the business need not be established in the EU. GDPR fines are one of the highest in the world, and their extraterritorial reach makes compliance a priority.
The LGPD (Lei Geral de Proteção de Dados) of Brazil and the GDPR (General Data Protection Regulation) of the European Union are both comprehensive data protection laws with similar goals, but they have some key differences. Here are three of the biggest:
-
Lawful Bases for Processing:
- GDPR: Provides 6 lawful bases for processing personal data (e.g., consent, contract, legal obligation, vital interests, public task, legitimate interests).
- LGPD: Includes 10 lawful bases, adding some specific to Brazilian contexts, such as “protection of credit” and “research by public study entities.” This means there might be situations where processing is allowed under LGPD but not GDPR.
-
Data Protection Officer (DPO) Requirements:
- GDPR: Requires DPOs to be appointed only in specific circumstances, such as when processing is large-scale or involves sensitive data.
- LGPD: Article 41 requires a controller to appoint an officer (encarregado), but ANPD Resolution CD/ANPD No. 2/2022 waives that duty for small processing agents. It is not required of every controller regardless of size. This is a significant difference, making DPOs more widely required in Brazil.
-
Data Breach Notifications:
- GDPR: Sets a strict 72-hour deadline for notifying the supervisory authority of a data breach.
- LGPD: LGPD Article 48 requires notice to the national authority and the data subject in a reasonable time period as defined by the authority. ANPD Resolution CD/ANPD No. 15 of 24 April 2024 set that period at three business days after the controller learns the incident affected personal data (six business days for small processing agents). This difference can affect how quickly and transparently organizations need to respond to breaches.
Differences in Principles
Data protection laws provide for processing principles, requirements, or lawful bases for processing and data subject rights. On these core provisions, the GDPR and the LGPD are similar. However, they differ in the nuances contained in the core provisions.
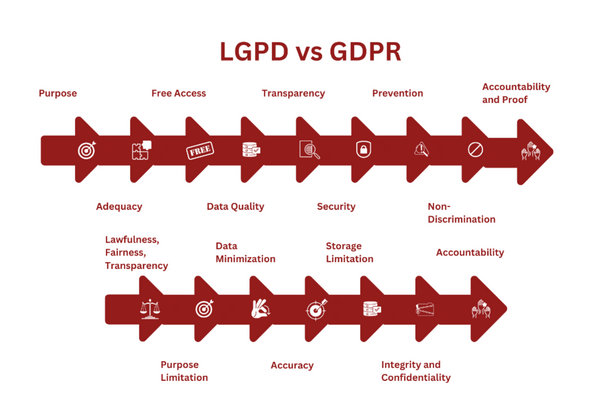
For instance, the GDPR contains seven principles on data processing principles, while the LGPD contains ten principles.
Data processing under the GDPR must adhere to these seven principles: lawfulness, fairness, and transparency; purpose limitation; data minimization; accuracy; storage limitation; integrity and confidentiality; and accountability.
Data processing under the LGPD must adhere to these ten principles: purpose, adequacy, necessity, free access, data quality, transparency, security, prevention, nondiscrimination, and accountability.
Differences in Data Subject Rights
Data subject rights in Brazil LGPD vs GDPR are the same with little differences. Perhaps, the GDPR’s data subject rights are broader depending on interpretation.
The right of access, right to rectification, right to erasure, right to data portability, right to object, and right related to automated processing are covered in both laws with different applications. Unlike the GDPR, the LGPD does not provide for the right to restriction of processing.
Differences in Justification
As a general rule, any processing of personal data is prohibited unless justified. For the GDPR, a business needs a lawful basis to process data. The equivalent of lawful basis in the LGPD is requirements.
On this point, the LGPD’s coverage is broader than the GDPR. All the lawful bases for processing under the GDPR are found in the LGPD, but some requirements for processing under the LGPD are not contained in the GDPR.
Both laws provide for consent, contract, legal obligation, vital interest, public task, legitimate interest and health (partly though for the GDPR) as acceptable reasons for processing personal data. In contrast, the LGPD provides for research, legal rights and credit as additional requirements.
LGPD vs GDPR Similarities & Differences
At first the LGPD seems a replica of the GDPR, but a closer analysis shows slight differences further highlighted by the choice of wording and interpretation.
Extraterritorial Scope
Both LGPD and GDPR have extraterritorial scope, bringing businesses outside Brazil and the EU under their jurisdiction.
Both the GDPR and the LGPD can apply to organizations outside the EU and Brazil. GDPR Article 3 covers processing in the context of an establishment in the Union and, if there is no such establishment, processing of personal data of people who are in the Union that relates to offering them goods or services or monitoring their behavior in the Union. LGPD Article 3 covers processing carried out in Brazil, processing aimed at offering or providing goods or services or at processing data of individuals located in Brazil, or personal data collected in Brazil. Residency and citizenship are not the test, and the LGPD does reach offering goods or services to individuals located in Brazil.
Data Processing Principles
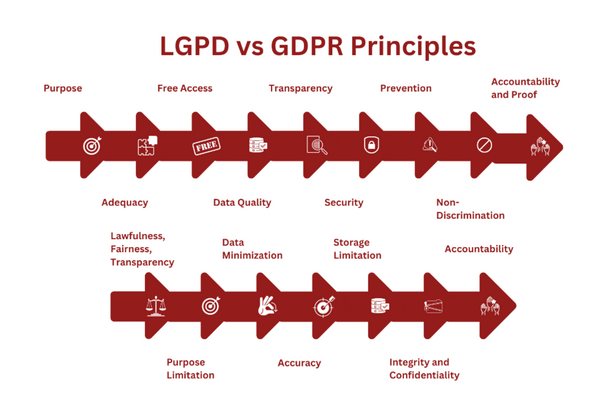
GDPR provides for seven processing principles, while LGPD provides for ten. GDPR’s lawfulness, fairness and transparency principles are not mentioned in LGPD. However, LGPD’s principles of transparency, prevention and non-discrimination mirror similar concepts.
GDPR’s data minimisation principle is absent in the LGPD. However, LGPD’s principle of necessity mirrors a similar concept. The GDPR’s storage limitation principle is not mentioned in the LGPD. However, the LGPD’s principle of necessity can be further interpreted to cover a similar concept.
The data security principle of the LGPD mandates businesses to keep personal data secure. The integrity and confidentiality principle covers data security in the GDPR. Both laws provide for access to data by data subjects. The LGPD calls it the free access principle, while the GDPR calls it the right of access.
The LGPD’s principle of prevention prohibits the processing of personal data to cause harm. While prevention is not mentioned in the GDPR, the lawfulness, fairness and transparency principle covers similar concepts.
As a way to mitigate the impact of Weapons of Math Destruction (WMDs) and ensure non-discrimination, the GDPR mandates human intervention for automated processing and allows data subjects to opt-out. LGPD contains no similar provision.
Justification/Legal Basis
Under the LGPD and the GDPR, businesses need a justification or legal basis before processing personal data.
The LGPD refers to legal basis as requirements, while the GDPR refers to legal basis as lawful bases. The LGPD has about ten requirements for a legal basis, while the GDPR provides for about seven lawful bases.
On the legal basis of vital interests, the LGPD refers to this basis as “protection of life or physical safety”. The LGPD expressly mentions health as a legal basis. But considering “protection of life or physical safety” can also cover health, this could be considered duplication.
On the legal basis of public interests, the GDPR focuses on the task or activity, while the LGPD focuses on public authorities as a processor. The LGPD provides for research as a legal basis, while the GDPR mentions research as an exception to the need for a lawful basis for processing.
Like the research mentioned above, the GDPR mentions exercising legal rights as an exemption to the need for a lawful basis.
For the LGPD, exercising legal rights is listed as a legal basis with specific reference to the Brazilian Arbitration Law. Perhaps the most significant difference in justifications between both laws is that the LGPD provides credit protection as a justification, but the GDPR does not.
Age of Consent
In both laws, children cannot consent unless an adult does so. Both laws differ on the approved age for consent.
GDPR Article 8 sets 16 as the default age for a child to consent to an information-society service when processing is based on consent, and member states may lower that age to no less than 13. It is not a general age of consent for all GDPR processing. LGPD Article 14 requires processing of children’s and adolescents’ data in their best interest; parental or guardian consent in Article 14, paragraph 1, is for children (criancas), generally under 12 under the Statute of the Child and Adolescent, not a 13-to-18 self-consent band.
Data Subject Rights
Except in one instance, data subject rights in the LGPD and GDPR are identical. In both laws, data subjects have a right to a privacy notice. However, the contents are slightly different.
GDPR Article 12(3) requires a response without undue delay and within one month, extendable by two further months (about three months total) where necessary. LGPD Article 19 requires the controller to provide confirmation or access immediately in simplified format, or a clear and complete declaration within 15 days.
Both laws provide for the right to erasure. Covered in the GDPR as the right to be forgotten and in the LGPD within three Articles (5, 16, & 18). In the LGPD, controllers must delete excessive, unnecessary or unlawful data. And data subjects could request deletion if the data were obtained using consent as justification.
The right to data portability is present in both laws, but the LGPD subjects the availability of the right “to the regulation of the controlling agency”.
While the GDPR grants data subjects the right to object to data processing, especially where justified under consent or legitimate interests, the LGPD makes no such provision. However, data subjects can withdraw their consent under the LGPD. Only the GDPR provides for the right to restriction of processing. The LGPD does not.
Data subjects’ rights in relation to automated processing are interpreted differently under both laws. The GDPR has two interpretations.
Some businesses interpret it to mean a ban on the automated processing of personal data. Others interpret it to mean implementing Human in the Loop (HiTL). The LGPD has only one interpretation: mandating HiTL, human intervention, or review for automated decisions with irreversible impacts.
Privacy Notice
While not explicitly mentioned, both laws are thought to require a “privacy notice” that tells data subjects who they are, how they collect data, what data they collect and why it is collected.
Both require a privacy notice to contain the name and contact details of the data controller, the purpose for processing, the categories of third-party recipients, storage periods, data subject rights and the right to complain to the authority.
Under the GDPR, the privacy notice must inform data subjects of the justification for processing, while under the LGPD, notification of justification is not required. Under the GDPR, the privacy notice must list the categories of personal data processed, which is unnecessary under the LGPD.
Under the GDPR, businesses making international transfers of personal data must notify data subjects of what safeguards are in place for data protection.
This obligation is absent under the LGPD. The LGPD requires businesses to list the responsibilities of the controllers and processors in the privacy notice. These requirements are not necessary for the privacy notice under the GDPR, although the responsibilities are listed in the law.
Data Security
Data security is an obligation of the controller and processor under both the LGPD and the GDPR. The LGPD makes it mandatory for businesses to keep a data processing record. Under the GDPR, this is only necessary for businesses with over 250 employees.
The GDPR specifies data security obligations, including pseudonymizing and encrypting data at rest and in transit. The LGPD does not specify what data security obligations include, only mentioning that the data protection authority will guide.
To ensure data security, both laws mandate businesses processing sensitive personal data to conduct an impact assessment first.
Data Breach Notices
Businesses must report a data breach to the data protection authority within 72 hours for the GDPR and a reasonable time for the LGPD.
The content of this report/notice differs. The GDPR notice contains more details, while the LGPD notice needs just the type of data breached and the data subjects affected.
Enforcement and Penalties
The GDPR came into force in 2018, while the LGPD came into force in 2020. Under both laws, data subjects are allowed to enforce their rights in court. GDPR Article 37 requires a DPO in specified cases (public authorities, regular and systematic large-scale monitoring as a core activity, or large-scale processing of special-category or criminal-conviction data as a core activity). It is not merely optional. LGPD Article 41 requires controllers to appoint an officer, subject to the small-processing-agent waiver in ANPD Resolution 2/2022.
Fines under the GDPR range from €10 million ($11m+) – €20 million ($22m+) or 2% – 4% of global revenue. Fines under the LGPD include a simple fine of up to 2% of revenue in Brazil in the last fiscal year, excluding taxes, limited to R$50 million per infraction, and a daily fine that is also subject to that same R$50 million total cap (Article 52, II and III). The R$50 million figure is a cap, not the amount of each daily fine, so daily fines do not stack above that per-infraction limit.
How To Stay Compliant with GDPR and LGPD Now?
Most data protection laws resemble the GDPR because it provides an array of reasonable data privacy rights and rules. On the positive side, since most obligations overlap, your business may already be more than halfway compliant with regulations like the LGDP and just needs some tweaks.
At Captain Compliance, we take out the guesswork and provide all you need for holistic compliance at the snap of your fingertips. Contact us today for peace of mind, happy customers and booming business.
FAQs
Does the LGPD apply to my business?
There is a high chance the LGPD applies to your business because it has extraterritorial reach. LGPD applies if the processing is carried out in Brazil, if it is aimed at offering or providing goods or services or at processing data of individuals located in Brazil, or if the personal data were collected in Brazil (Article 3). Establishment in Brazil is enough under the first prong; an organization outside Brazil can also be covered without a nationality or residency test.
Does the GDPR apply in Brazil?
Like the LGPD, the GDPR also has extraterritorial scope. This means the GDPR can apply to a business in Brazil if it processes personal data of people who are in the Union in connection with offering them goods or services or monitoring their behavior in the Union (Article 3(2)), or if the processing is in the context of an establishment in the Union (Article 3(1)). Residency is not the test.
The GDPR can apply to a Brazilian business that offers goods or services to people who are in the Union or monitors their behavior in the Union (Article 3(2)). The LGPD likewise reaches processing aimed at offering or providing goods or services, or processing data, of individuals located in Brazil (Article 3, II). Neither law uses residency or citizenship as the test.
I already comply with the GDPR; do I still need to comply with the LGPD?
Yes. While most compliance obligations in both laws overlap, some differences and nuances remain. Captain Compliance can help you identify gaps you need to cover.
Learn more about the GDPR Principles.
What is the difference between the GDPR and the LGPD?
There are slight differences, often in wording and interpretation. For example, businesses can rely on ten legal bases under LGPD Article 7, while GDPR Article 6 provides six lawful bases for ordinary personal data.
What happens if I fail to comply with the LGPD?
Data subjects may seek redress in court for damages. Separately, ANPD may impose administrative sanctions under Article 52, including a simple fine of up to 2% of revenue in Brazil, excluding taxes, capped at R$50 million per infraction, and a daily fine that is also subject to that R$50 million total cap. The R$50 million figure is a cap, not the amount of each daily fine, and it is not what a private plaintiff recovers.
So it really does make sense to be compliant and not violate these privacy laws. Book a demo below to get started.
Put this into practice
Turn privacy guidance into working controls.
Captain Compliance helps teams discover tracking technologies, enforce consent, manage privacy requests and document the evidence behind every decision.